
CISOs beginning a new role, or changing sectors, can easily make the same mistake.
They walk in with years of experience, see what’s broken, and start fixing. By the end of week three, they’ve opened too many tickets and asked too many people to change too many things. They are quietly draining the trust account they’ll need to draw on for the next few years.
It’s an honest mistake. CISOs are often hired because something is broken. There is real pressure to demonstrate value. Their instinct to act is the instinct that got them the job in the first place.
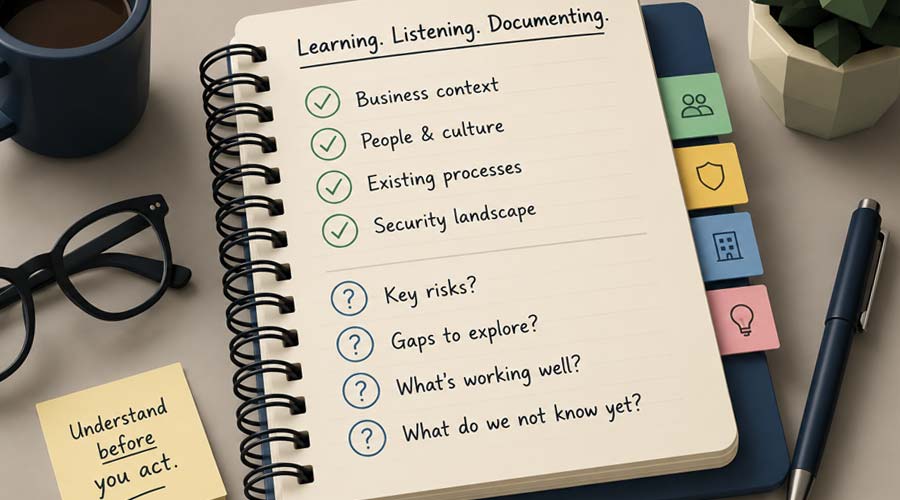
What if success in the first 90 days actually comes from listening, rather than fixing?
Why the instinct to fix is the wrong mindset for a new CISO
I had this exact conversation with Matt Martin, CISO at Western Carolina University, during our latest Strategic CISOs session. Matt spent two decades leading security in financial services before moving into higher education. He was honest about how his first month went:
Matthew Martin
CISO, Western Carolina University
“I jumped in and was like, ‘I know how this is supposed to work. That’s not how you’re supposed to do it. We need to fix that.’ And after like a month of that, I’d overloaded the entire university with stuff to go fix. Too many tickets. I did not make a lot of friends.”
“Go with the intention to learn. How do I provide value in a way that’s actually valuable to the other person? What I should have done was shut up and listen and document. Document, document, document.”
What the best new CISOs do in their first 90 days
- They start by listening. The IT leaders in any organization already know what’s not working. They’ve been living with the gaps. Their pain points can double as your risk register starting point.
As Matt described it: “go and have conversations with the leaders of the various teams within IT and just ask, hey, what’s not working, what are you having trouble with, what’s holding you back? Not just security, just technology in general.”
That dialogue is also where you build the cross-functional trust you’ll need later.
- They document inside a framework, not in spreadsheets. New CISOs get flooded with what feels like random spreadsheets flying at them. Convert that mess into structured risk language The framework doesn’t have to be perfect at first. What matters is that you’re treating risk as a discipline from week one rather than a backlog to triage later.
- They reframe decisions from people to use cases. This mindset shift is so effective. Matt described how access decisions in higher ed (and in plenty of enterprises) are often made one person at a time.
“You would approve something for some person to do this thing, but then you’d also evaluate and approve another person to do the exact same thing. Because it was based on a person versus based on a specific use case.”
The problem with person-by-person decisions is that they don’t scale. Each one is a fresh judgment call without documented rationale tying it to a consistent standard. Over time, you end up with a security program that’s effectively a collection of one-offs — impossible to audit cleanly, scale, or defend when something goes wrong.
Use-case thinking asks, “what’s the use case underneath this request, and what’s the right policy for it?” Once that’s defined, the decision applies consistently to anyone who fits the pattern. It’s documented and defensible.
How new CISOs build credibility and trust
Every interaction in the first 90 days is a deposit in a trust account you’ll need to draw on for the rest of your tenure.
CISOs who push too early run out of credibility before they’ve had a chance to build it. But by listening, they’ll be invited into the decisions that matter. They get the benefit of the doubt when they say something is a priority.
Matt reflected on what changed once he started listening:
“You’re showing them that you’re listening and you’re solving problems. And that trust is what helps you later on when you’re trying to push a little bit to do more things.”
This isn’t only a higher education lesson. It applies to anyone leading security in an environment where influence matters more than authority: decentralized organizations, matrix structures, or regulated industries with strong line-of-business autonomy.
The mindset that defines strategic CISOs
Matt and I talked about a lot during our session: How to translate security into language your board understands. Why use cases beat people-by-people decisions. What kinds of CISOs are going to thrive in higher ed and beyond.
Of all those topics, his emphasis on order of operations and mindset is critical. Technical skills are essential, but listening earns you the trust to apply it. Listen first and fix later.
Watch the full conversation with Matt Martin on demand here.
FAQ
What should a new CISO do in their first 90 days?
The strongest new CISOs spend their first 90 days listening rather than fixing. That means talking to IT and business leaders about what’s not working, documenting risks inside a framework rather than reacting to scattered requests, and building the cross-functional trust they’ll need to drive larger changes later. The instinct to demonstrate value through action is real, but the CISOs who push too hard too early often lose the credibility they need to lead effectively.
Is it better to start with risk or compliance as a new CISO?
Risk, every time. If you manage risk well, compliance follows. Starting with compliance forces a checkbox mindset that’s hard to shake, and it doesn’t tell you what actually matters to the business. Starting with risk gives you a framework for prioritization and a language your leadership can engage with.
How long does it take a new CISO to build credibility in a new organization?
The first 90 days are foundational, but credibility compounds over the first 12 to 18 months. CISOs who spend their early weeks listening, documenting, and showing they understand the existing landscape build trust faster than those who try to make sweeping changes immediately. The trust earned in the first quarter is what makes larger changes possible later, and gives you clarity on which projects will actually protect the business.
