

In a recent roundup of strategic initiatives for CISOs, I argued that continuous assurance is the 2026 operating model. Across all ten initiatives, the pattern was clear. Security is no longer being evaluated by effort, it’s being evaluated by outcomes.
Boards, customers, and regulators are no longer asking what tools you deployed or how busy your security team is. They are asking a simpler, harder question: Can you prove that your controls are working right now?
Every security leader wants to confidently say “yes.” However, if you want to attain continuous assurance and clearly demonstrate the outcomes of your security program, it will only be possible with a foundation of continuous control monitoring. The two go hand-in-hand.
Continuous assurance only works if controls are continuously monitored
Let’s ground this in practical terms.
Continuous control monitoring (CCM) is an ongoing, real-time approach to overseeing the performance of IT controls. CCM allows you programmatically validate that critical security and compliance controls are operating as intended, across systems that matter.
Continuous assurance or security assurance is the outcome that the business experiences: confidence that security posture, resilience, and compliance claims are provable without rebuilding evidence from scratch. It’s a posture displaying that controls are effective, compliant, and aligned to business commitments.
The distinction is important. Confident security assurance is the goal, and continuous control monitoring is what makes it achievable.
Without CCM, assurance can only be retrospective. It must be reconstructed during audits, customer reviews, incidents, or board prep. That’s where teams lose time, credibility, and momentum.

Tired of manual risk assessments that leave your board exposed?
Automate IT risk quantification with TrustCloud and confidently minimize CISO and Board liability.
Learn MoreWhy CCM has become a CISO priority in 2026
A few pressures come up repeatedly when I talk to CISOs and read the security headlines.
- The cost of failure keeps rising.
IBM’s 2025 Cost of a Data Breach Report showed the global average breach cost climbing to nearly $5M, the largest increase in years. Tolerance for uncertainty is running low. “We think” is no longer an acceptable answer. - Third-party risk has become a common cause of breaches.
Verizon’s Data Breach Investigations Report continues to highlight how frequently incidents involve vendors, partners, and software supply chains. Third-party risk shifts and changes much faster than point-in-time questionnaires can address. - Disclosure expectations are non-negotiable.
With the SEC’s cybersecurity incident disclosure rules in effect, organizations must explain what happened, what changed, and what they are doing next. That’s extremely difficult if control evidence is assembled after the fact. - Security frameworks require accountability.
NIST CSF 2.0 elevated “Govern” to emphasize cybersecurity as a business risk management function, not just a technical discipline. That shift demands evidence, trend lines, and decision-ready reporting.
All of this points to the same conclusion: security programs need live control evidence, not snapshots.
What continuous control monitoring looks like in practice
CCM is not about monitoring everything. It’s about continuously validating the controls that, if they fail, would negatively impact that business.
In practice, CISOs are prioritizing monitoring across areas like:
- Identity: phishing-resistant MFA coverage, privileged access drift, and lifecycle management for service accounts and AI agents.
- Cloud environments: guardrails and misconfiguration prevention tied to production systems that change daily.
- Vulnerability and exposure management: tracking remediation time for critical assets, not just scan volume.
- Third-party risk: continuous signals for high-blast-radius vendors instead of annual attestations.
- Resilience: evidence that backups are tested, restore drills are executed, and recovery objectives are trending in the right direction.
- AI governance: inventories of AI usage, policy enforcement, logging, and auditable controls tied to real systems.
Continuous monitoring is most powerful when it is mapped to systems, data, and commitments that actually matter.
What CCM unlocks for the business
When controls are continuously monitored, assurance stops being a periodic exercise (focused on passing the audit) and becomes an operating capability, and a strategic differentiator. With CCM in place, you can unlock three key outcomes.
Protect
You reduce the likelihood of breaches by identifying drift or vulnerabilities early, before they compound into exposure.

Sravish Sridhar
CEO, TrustCloud
“Think of continuous testing as your Apple Watch – it tells you when something might be wrong before it becomes critical.”
Withstand
Resilience becomes measurable. You can show that recovery plans are tested, owned, and improving over time, not just documented. And if a breach does occur, you can ensure rapid containment and response.
CSO’s 2026 interviews show a greater focus on whether organizations can continue operating during disruption. That changes the work, requiring resilience to be measurable, with tested backups, verified restore capability, and tracked recovery objectives.
Prove
Audits, customer reviews, and board reporting become focused and faster, showcasing current evidence in meaningful ways. You can shift your reporting from backwards-looking activity to forward-looking business impact, earning credibility for the security function.
How CISOs can start without rebuilding everything
Adopting continuous control monitoring does not require replacing your GRC systems. It requires transforming how they operate.
The shift begins by moving from calendar-driven audits to trigger-driven automation. Instead of asking, “What do we need for next quarter’s audit?” ask, “What changed in our environment today?”
Chapter 4 of our 2025 CISOs’ Guide to Automate Security, Privacy, and AI Risk Assessments outlines a phased approach focused on automation:
- Identify high-impact objectives tied to revenue, regulation, and resilience.
- Map controls programmatically to a unified control framework.
- Automate evidence ingestion from identity, cloud, vulnerability, and ticketing systems.
- Trigger testing when risk thresholds shift.
- Measure outcome improvements, not ticket volume.

Tejas Ranade
CPO, TrustCloud
“The time and cost required to get full visibility manually are prohibitively high. Automation is the only solution.”
Continuous control monitoring is not about adding more manual oversight. It’s about eliminating it. For a deeper implementation timeline and key dashboards to establish, read the full 2025 CISOs’ Guide.
Continuous control monitoring is how assurance becomes real
If continuous assurance is the operating model for 2026, CCM is the mechanism that sustains it.
Legacy GRC manages paperwork, but security assurance mitigates risk.
CISOs who adopt CCM are not modernizing audits. They are transforming GRC into a proactive, AI-native, data-driven discipline that supports resilience, accelerates revenue, and strengthens board confidence.
The teams that will protect, withstand, and prove continuous assurance will not do more manual work. They will produce more trust with far less friction.
Making CCM stick: Building the human infrastructure behind the technology
Continuous control monitoring succeeds or fails not just on the strength of the tooling, but on whether the right people are aligned around the right signals. Many CCM rollouts stall not because the technology is wrong, but because control ownership remains ambiguous, engineering teams don’t know they’re responsible for certain controls, and GRC teams lack the context to interpret what automated tests are actually surfacing.
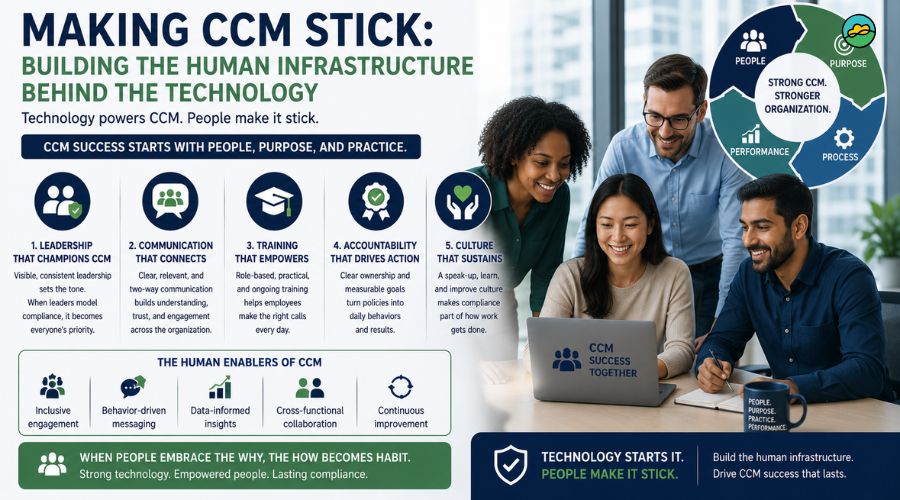
The most effective CCM programs treat ownership as a design requirement, not an afterthought. That means mapping every monitored control to a named owner before automation goes live, establishing clear escalation paths when a control drifts or fails, and ensuring those owners receive alerts in the tools they already use, whether that’s a Jira ticket, a Slack message, or a dashboard they check daily. When accountability is embedded into existing workflows, CCM stops feeling like surveillance and starts feeling like shared responsibility.
The cultural shift that CCM demands is also worth naming directly: it requires moving security teams from a reactive posture, fixing things when audits reveal gaps, to a proactive one where drift is flagged and resolved before it compounds. That shift only holds if leadership reinforces it. CISOs who communicate CCM findings in board and executive reporting, not just as technical metrics but as business signals tied to risk reduction and resilience, create the organizational gravity that sustains the program.
When business leaders see continuous control data informing strategic decisions rather than buried in GRC reports, the security function earns a different kind of credibility. CCM then becomes less about proving compliance and more about demonstrating that the organization’s defenses are alive, tested, and accountable, which is precisely the assurance that boards, regulators, and customers are demanding in 2026.
How AI is changing what continuous control monitoring can actually detect
Traditional continuous control monitoring tools have largely focused on binary pass/fail checks, confirming whether a configuration setting is enabled or a control owner has completed a required task. AI-powered monitoring is pushing this capability significantly further. Rather than simply flagging that a control failed, machine learning models trained on historical control performance can identify subtle behavioral drift before a failure actually occurs, such as access permissions gradually expanding beyond policy or logging configurations slowly degrading across a fleet of cloud instances. This shifts CCM from a detection mechanism into a genuine early-warning system, giving security teams the lead time to intervene before an exploitable gap becomes a real incident.
This evolution matters because the volume and complexity of controls most enterprises must monitor has outpaced what manual review or simple rule-based automation can realistically handle. AI-driven CCM platforms can correlate signals across hundreds of controls and systems simultaneously, surfacing patterns that would be invisible when reviewing controls in isolation, for instance, identifying that a cluster of failed access reviews consistently correlates with a specific onboarding workflow gap.
For CISOs building their 2026 monitoring strategy, the question is no longer whether AI belongs in CCM but how quickly it can be operationalized to keep pace with an environment where threats and infrastructure are both changing faster than any manual process can track.
References
- CSO Online, Cybersecurity leaders’ resolutions for 2026 (Jan 5, 2026). https://www.csoonline.com/article/4110151/cybersecurity-leaders-resolutions-for-2026.html
- IBM Security. (2025). Cost of a data breach report 2025. https://www.ibm.com/reports/data-breach
- National Institute of Standards and Technology. (2024). The NIST cybersecurity framework (CSF) 2.0. https://nvlpubs.nist.gov/nistpubs/CSWP/NIST.CSWP.29.pdf
- TrustCloud. (2025). 2025 CISOs’ guide to automate security, privacy, and AI risk assessments. https://www.trustcloud.ai/2025-ciso-guide-to-automate-security-privacy-and-ai-risk-assessments/
- Verizon. (2025). 2025 data breach investigations report. https://www.verizon.com/business/resources/reports/dbir/
- U.S. Securities and Exchange Commission. (2024). Cybersecurity incident disclosure: Key considerations for public companies (speech). https://www.sec.gov/newsroom/speeches-statements/gerding-cybersecurity-incidents-05212024
FAQs
What is continuous control monitoring (CCM) and how does it differ from continuous assurance?
Continuous control monitoring (CCM) is an ongoing, real-time approach to overseeing the performance of IT controls, allowing organizations to programmatically validate that critical security and compliance controls are actually operating as intended across the systems that matter most. Rather than checking a control’s status once during a periodic audit, CCM continuously pulls evidence from live systems to confirm controls remain effective at all times, not just on the day an auditor happens to look.
Continuous assurance, by contrast, is the outcome the business experiences as a result of that monitoring, the confidence that security controls are working, demonstrated through verifiable, real-time evidence rather than point-in-time snapshots.
The two concepts are deeply interdependent: continuous assurance is impossible to achieve without continuous control monitoring as its foundation. You cannot credibly tell a board, customer, or regulator that your controls are working right now unless you have a monitoring system in place that is actually validating that claim in real time, which is precisely why the two operate hand-in-hand as a unified 2026 security operating model.
Why has continuous control monitoring become a top priority for CISOs in 2026?
Continuous control monitoring has risen to the top of the CISO priority list because the expectations placed on security leaders have fundamentally shifted. Boards, customers, and regulators are no longer satisfied with hearing about the tools a security team deployed or how much effort was invested; they are asking a simpler and far harder question: can you prove that your controls are working right now?
This outcome-based standard of evaluation makes periodic, point-in-time audits insufficient, since a control that passed an audit six months ago provides no real evidence of its current state.
This shift reflects the broader reality that threats, infrastructure, and regulatory requirements are all evolving faster than annual or quarterly audit cycles can keep pace with. A control gap that emerges the day after an audit concludes can remain undetected for months under a traditional periodic model, creating a dangerous blind spot.
CCM closes that gap by validating control performance continuously rather than intermittently, which is why it has become the foundational requirement for any CISO aiming to demonstrate genuine, defensible security assurance rather than simply checking a compliance box.
How is AI changing what continuous control monitoring is capable of detecting?
AI is expanding continuous control monitoring well beyond simple binary pass/fail checks that confirm whether a setting is enabled or a task has been completed. Machine learning models trained on historical control performance data can now detect subtle behavioral drift before an actual failure occurs; for example, identifying that access permissions are gradually expanding beyond policy limits or that logging configurations are slowly degrading across a fleet of cloud instances over time. This transforms CCM from a reactive detection tool into a genuine early-warning system, giving security teams the lead time needed to intervene before a gap becomes an exploitable vulnerability.
This capability is increasingly necessary because the sheer volume and complexity of controls modern enterprises must monitor has outpaced what manual review or basic rule-based automation can realistically manage.
AI-driven CCM platforms can correlate signals across hundreds of controls and systems simultaneously, surfacing patterns that would remain invisible if each control were reviewed in isolation. For CISOs building out their monitoring strategy, AI is no longer an optional enhancement — it is becoming essential to keeping pace with an environment where both threats and infrastructure change faster than manual processes can track.
