Replace manual risk assessments by translating 1st- and 3rd-party security signals into strategic risk management.
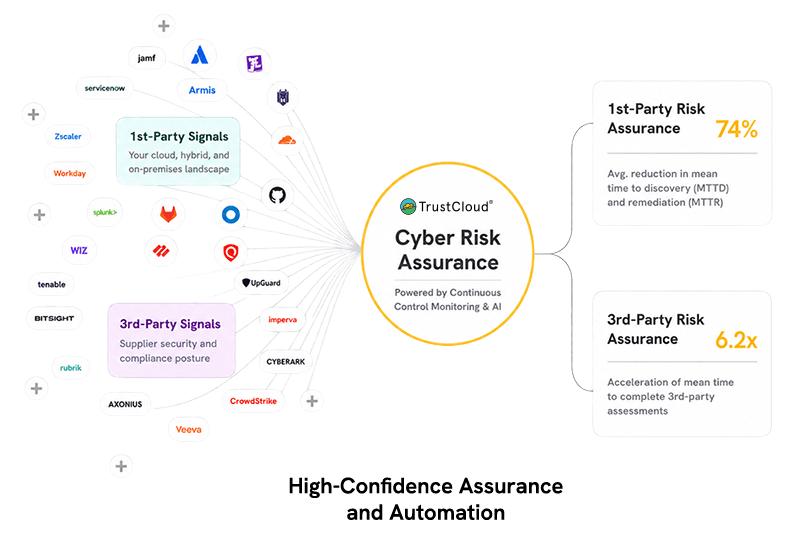
TrustCloud is the only company that brings together 1st- and 3rd-party risk assessments in a continuous, data-driven engine, so your posture has a pulse.
Value delivered for Fortune 500 and Global 2000 CISOs across regulated industries.
10%
of risk landscape monitored continuously vs. 20% industry standard
10%
average reduction in mean time to discovery (MTTD) and remediation (MTTR)
10%
of vendors assessed, in days not weeks vs. 20% coverage with manual reviews
1x
acceleration of mean time to complete 3rd-party assessments
Where TrustCloud delivers value
Top four ways security leaders use TrustCloud.
01
Prove your digital crown jewel applications are operating securely.
Every control on every digital crown jewel application, tested continuously against live data instead of a point-in-time sample twice a year. Each failing control carries an owner, an SLA, and a dollar figure — so the answer is a number, not conjecture.
02
Move 3rd-party risk beyond assessments into data-driven prediction and prioritization.
Agentic assessments combine outside-in feeds, public and dark web signals, and inside-out evidence from the vendor itself, then rank vendors by the risk they carry into your digital crown jewel applications. A ranked list of vendors, not another security questionnaire.
03
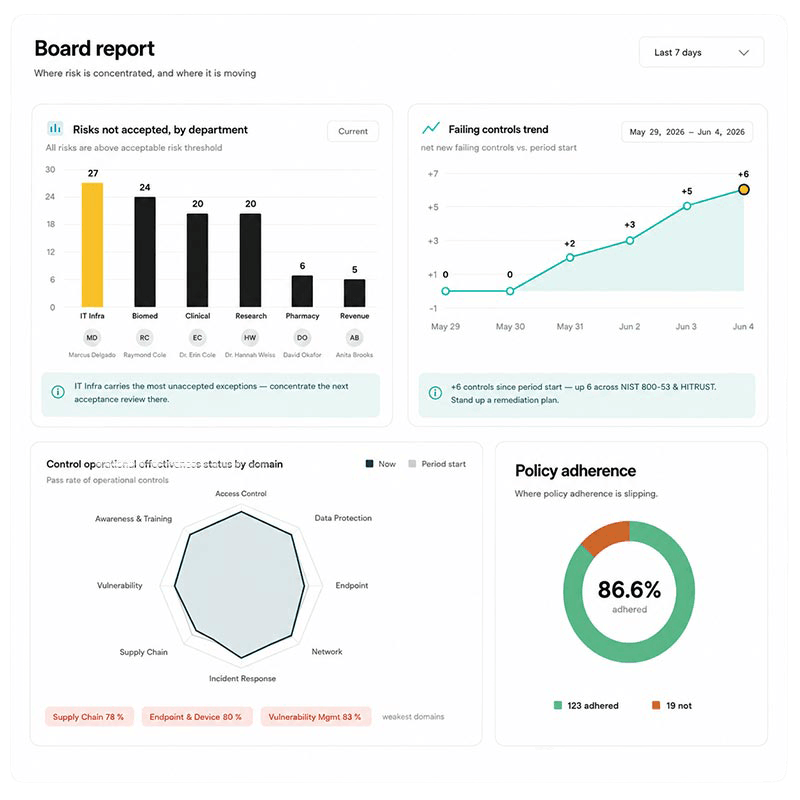
Show your board the business impact of your security program.
Residual risk in dollars, mapped to the business goals your CEO and board already care about. Reporting is built the way each audience reads it — the CIO version, the risk committee version, the regulator version — from one set of underlying data.
04
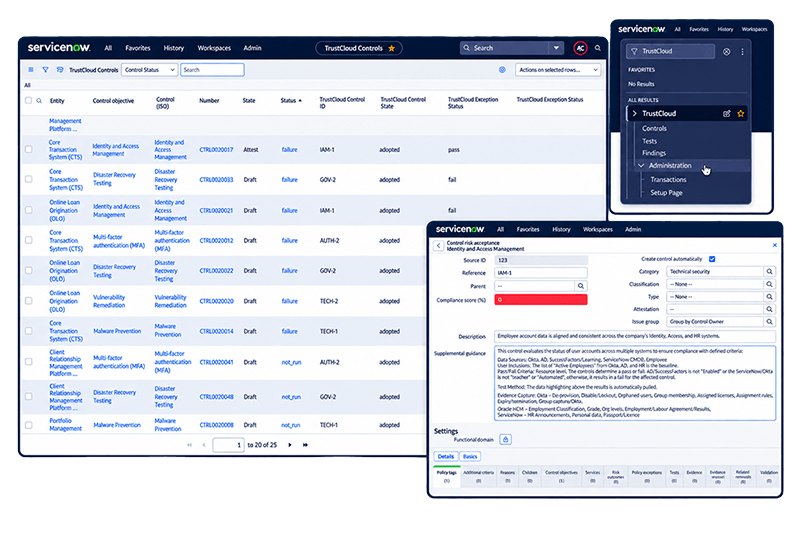
Automate Continuous Control Monitoring for ServiceNow IRM — so IRM doesn’t sit on the shelf.
IRM customers already own the system of record. What they don’t have is the automation layer that keeps it populated with continuously tested, cited, current control results. TrustCloud is ServiceNow-native, and ServiceNow is both a strategic investor and a customer.
The differentiated technology that delivers cyber risk assurance.
Continuous Control Monitoring
Assurance comes from Continuous Control Monitoring: proving a control is operating effectively, then mapping that control to the risk it mitigates. Live data in, deterministic test, cited verdict — re-run on every change and on schedule, built on a common control framework.
Structured and unstructured data from any source, transformed into one schema.
Automate any control
Technical, documentation, and process controls — not only the ones with an API.
Verify any objective
Test any governance, risk, compliance, or contractual objective against live evidence.
Test at scale in hybrid environments
Cloud, hybrid, and on-premises, including homegrown applications, at enterprise volume.
Assurance AI
People-led, assurance- and impact-driven. Every agent is purpose-built for one job, grounded in your data and controls, and requires human approval before it acts. Every answer is cited, scored for confidence, and auditable — AI that can defend its own work. Assurance comes from Continuous Control Monitoring: proving a control is operating effectively, then mapping that control to the risk it mitigates. Live data in, deterministic test, cited verdict — re-run on every change and on schedule, built on a common control framework.
Purpose-built agents across the first, second, and third lines of defense, adapting to your frameworks and workflows.
Deterministic
A rules engine drives the AI. TLS ≥ 1.2 is a pass or a fail, not a probability.
Built-in assurance
Every action cited, scored, and auditable, so results stand up to an auditor and a regulator.
Proves business impact
Tracks the time and cost it saves, and reports that ROI in real time.
Why TrustCloud is different
The only company doing continuous, data-driven analysis of 1st- and 3rd-party signals — mapped to risk.
Every other approach picks a side. Security tools watch your applications but can’t prove a control is operating. Security ratings score your vendors but never see inside them. Point-in-time assessments cover both twice a year, and that gets called a program. TrustCloud analyzes your applications and your vendors continuously, and maps what it finds to the risk it actually creates for the business.
Continuous, not point-in-time
Controls tested on every change and on schedule, so posture is current, not accurate as of last quarter.
Data-driven, not survey-driven
Millions of live data points from your environment and those of your suppliers, not a security questionnaire and a signature.
Mapped to risk, not check-the-box
Every signal maps through the control graph to the risk it mitigates and the business impact it carries.
Value doesn’t wait for the end of the rollout
Get go-live assurance in six months.
Month 1: Kick-off
Control graph live
Integrations turned on across your critical systems. Control graph live. Initial objectives and scope defined.
low-confidence + automation
Months 1–3: Initial value unlock
50% of objectives achieved
Proof of high-confidence assurance, gap dashboards live, and business units engaging with results they can see.
50% of in-scope assets
Months 3–6: Programmatic assurance
Full scope under assurance
Full set of initial objectives achieved, validated automation assurance, and live business-impact reporting built the way you want it.
high-confidence assurance + automation → 100%
First controls operational in weeks.
Weeks, not years. That’s the model.
One common thread
The common thread is trust.
Continuous monitoring of your 1st- and 3rd-party signals makes trust measurable — and provable, internally and externally, so security drives the business instead of chasing it.