

Continuous audit readiness is a commitment to excellence, a promise to regulators, investors, employees, and customers that your organization operates with the highest standards of integrity, efficiency, and foresight. Embrace the journey, and let continuous audit readiness be the cornerstone of your business strategy in the digital age.
For further insights and tailored strategies to implement continuous audit readiness in your organization, consider engaging with industry experts who specialize in integrating these transformative practices into corporate governance structures. The future of compliance is continuous, and the time to act is now.
In this article, we will explore the leadership perspective on continuous audit readiness, its multifaceted business benefits, and how it aligns with diverse compliance frameworks such as ISO standards, HIPAA, SOX, PCI-DSS, and GDPR. Our discussion provides practical examples and case studies and outlines key operational goals that business leaders can achieve by adopting continuous audit readiness practices.
What is continuous audit readiness?
Continuous audit readiness is an evolving management discipline that integrates real-time monitoring, routine automated tests, and ongoing compliance verification into the daily operations of an organization. Rather than preparing for audits on an occasional or annual basis, continuous audit readiness encourages embedding control and compliance practices at the core of business processes. The goal is to create an environment where compliance is always current, risk management is proactive, and decisions are data-driven.
The evolution of audit practices
Historically, audits were treated as occasional events, often annual or semi-annual exercises that focused on checking boxes and verifying compliance at a specific point in time. While this snapshot approach provided some visibility, it left organizations vulnerable to gaps that could emerge between audits. In today’s fast-paced business environment, where regulations, technologies, and operational processes are constantly shifting, waiting for the next audit to uncover issues is no longer viable. Organizations that continue to rely solely on periodic reviews risk compliance failures, operational inefficiencies, and reputational damage.
The move toward continuous readiness represents a fundamental change in how audits are perceived and executed. Rather than being a reactive, checklist-driven task, audit readiness becomes an ongoing, integrated process embedded into everyday operations. This proactive approach allows organizations to identify gaps in real time, prioritize risk mitigation, and allocate resources more effectively. By adopting continuous monitoring, automated controls, and real-time reporting, leaders can stay ahead of regulatory changes, address security vulnerabilities promptly, and align compliance practices with evolving business strategies. Ultimately, organizations that embrace continuous readiness not only reduce risk but also strengthen operational resilience and strategic agility.

Looking for automated, always-on IT control assurance?
TrustCloud keeps your compliance audit-ready so you never miss a beat.
Learn MoreUnderstanding continuous audit readiness
Continuous audit readiness describes a mode of operation where organizations maintain an ever-present state of preparedness, ensuring that all systems, processes, and controls are perpetually audit-ready. Traditionally, audits have been viewed as periodic events, usually annual or biannual reviews conducted either internally or by third-party entities. However, with the explosion of data and technological adoption, reliability and compliance can no longer be verified solely via point-in-time reviews.
Modern continuous audit readiness extends beyond mere data recording or periodic sampling. Companies are now embedding technological tools that provide real-time data analytics and risk assessments. For example, software applications and integrated systems can track transaction flows, flag unusual patterns immediately, and provide automated alerts for potential discrepancies. This proactive detection not only minimizes the possibility of non-compliance but also enhances the organization’s overall risk management strategy.
Ultimately, continuous audit readiness is about adopting a mindset that expects every aspect of the organization to be ready for scrutiny at all times. When this philosophy is adopted at every operational level, it can facilitate smoother audits, reduce response times to regulatory queries, and even preclude the need for costly remedial actions. The continuous nature of these processes means that the organization can address issues swiftly, often before they escalate into more severe compliance risks.
Key components of continuous audit readiness
Continuous audit readiness is more than a compliance objective; it is a discipline that strengthens how an organization operates every day. Instead of waiting for annual reviews, teams rely on systems and habits that keep them prepared at all times. This shift demands flexible structures that can adjust to changing regulatory expectations while maintaining strong oversight of risks.
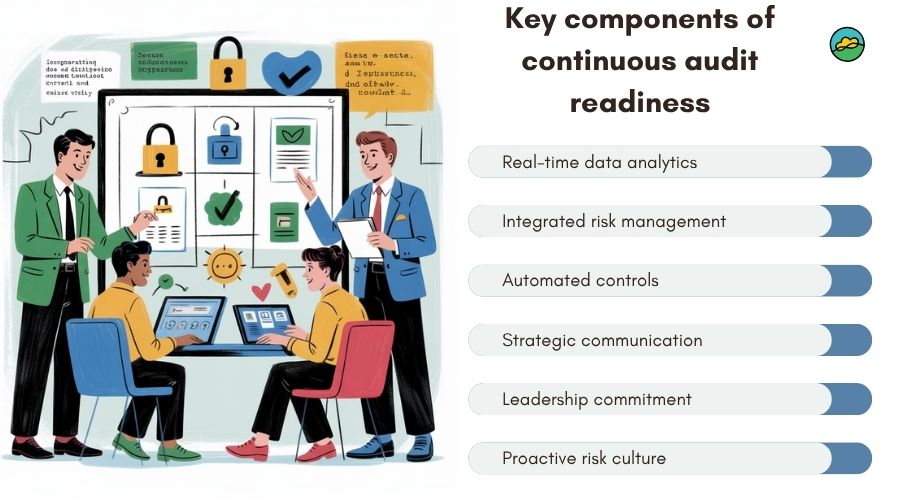
By combining technology, collaboration, and proactive controls, organizations create an environment where issues surface early and decisions are grounded in reliable data. When these elements work together, audit readiness becomes a natural part of daily workflows instead of a rushed, last-minute effort.
1. Real-time data analytics
Using real-time analytics gives teams instant visibility into financial activities, operational events, and security indicators. These insights help identify unusual patterns before they escalate into issues. Continuous monitoring also strengthens decision-making because leaders rely on current, trustworthy data instead of outdated reports. With advanced tools working in the background, organizations gain early warnings that support a smoother, more predictable audit experience.
2. Integrated risk management
Bringing all risk assessments under a unified framework allows every department to operate from the same playbook. This alignment removes silos, reduces duplicated work, and ensures that risks are evaluated consistently. When risk insights support strategic objectives, leaders can prioritize actions with clarity. The result is a comprehensive view of threats and controls that makes audit preparation more structured and reliable.
3. Automated controls
Automation helps ensure controls function consistently without manual intervention. Systems can validate data continuously, surface suspicious activities, and quickly alert teams when thresholds are breached. This reduces human error and frees staff from repetitive tasks. Automated controls not only maintain accuracy but also accelerate how quickly issues are resolved, creating a strong foundation for keeping audit readiness intact at all times.
4. Strategic communication
Strong communication ensures that compliance expectations are understood across all teams involved. When auditors, risk managers, and department leaders share updates promptly, it becomes easier to correct problems before they grow. Open channels also encourage transparency, which strengthens trust across the organization. With clear direction and active participation from all sides, continuous readiness becomes an achievable and sustainable practice.
5. Leadership commitment
Leadership sets the tone for how seriously audit readiness is treated. When executives support investments in technology, training, and process improvement, teams stay motivated and engaged. A committed leadership team reinforces expectations, removes roadblocks, and ensures that compliance goals align with business priorities. This steady guidance helps embed continuous readiness as an organizational value rather than a temporary project.
6. Proactive risk culture
A proactive mindset encourages teams to identify risks early instead of reacting after problems surface. This culture values vigilance, learning, and responsible decision-making. When employees understand how their actions influence compliance outcomes, they naturally contribute to stronger controls and better documentation. Over time, this shared awareness helps reduce disruptions, strengthens audit outcomes, and builds a more resilient operating environment.
Embedding continuous audit readiness into everyday operations transforms how an organization manages compliance. When real-time insights, automation, collaboration, and leadership alignment come together, teams no longer scramble to meet audit deadlines. Instead, they operate with confidence, knowing that risks are monitored and addressed throughout the year. This forward-looking approach reduces costs, improves efficiency, and strengthens trust with regulators, customers, and stakeholders.
Read the “ISO Standards and their Internal Audit (IA) requirements” article to learn more!
Business benefits of continuous audit readiness
Maintaining continuous audit readiness is no longer just a compliance requirement; it has become a strategic advantage. Organizations that embed audit preparedness into daily operations gain visibility into their controls, processes, and risk landscape in real time. This proactive stance reduces the likelihood of compliance failures while also improving operational efficiency by streamlining workflows and minimizing last-minute scrambles before audits. From a leadership perspective, continuous readiness provides actionable insights that support better decision-making, enabling executives to allocate resources wisely, anticipate regulatory changes, and align security and compliance initiatives with broader business objectives.
Beyond risk mitigation, continuous audit readiness also strengthens stakeholder confidence. Clients, partners, and investors see a company that is disciplined, transparent, and capable of managing risks effectively, which can translate into faster contract approvals, stronger business relationships, and a competitive edge in the market. It also encourages a culture of accountability within the organization, where teams are regularly monitoring and improving processes rather than reacting to periodic audits. Ultimately, this approach transforms compliance from a reactive obligation into a forward-looking, value-generating capability that benefits both operational performance and long-term business growth.
- Enhanced Risk Management and Mitigation
For business leaders, understanding and mitigating risks is a core responsibility. Continuous audit readiness facilitates enhanced risk management by- Early Detection of Anomalies: Real-time monitoring identifies outliers and potential compliance infractions as they occur, allowing for immediate resolution. For instance, if a financial control procedure in line with SOX requirements falters, the system can instantly alert management to prevent further escalations.
- Increased Transparency: Routine audits that track the compliance over time create a transparent operational framework for decision makers, reducing the ambiguity that often clouds risk management assessments.
- Rapid Remediation: With continuous readiness, the timeline for remediation significantly shortens. Organizations can solve identified issues before they snowball into more significant risks or attract regulatory penalties.
This proactive risk management strategy enables leaders to make more informed decisions and build resilience into their corporate strategies.
- Improved Operational Efficiency and Reduced Costs
The continuous integration of audit processes promotes operational efficiency by reducing the sunk costs associated with traditional periodic audits. Key operational efficiencies include- Streamlined Processes: Automation of routine audit tasks reduces redundancies, freeing up valuable resources that can be redirected to other strategic areas of the business. For example, automated workflows for compliance checks under frameworks such as ISO 27001 or GDPR allow IT teams to focus on strategic cybersecurity initiatives.
- Reduced Audit Fatigue: Rather than undergoing prolonged audit preparations, organizations maintain a state of readiness at all times, thus eliminating the high labor costs and disruptions associated with ‘big-bang’ audits.
- Cost Efficiency: Early detection of issues decreases the likelihood of incurring costly fines, legal expenses, and remediation efforts following compliance breaches.
Leaders who invest in continuous audit readiness are often rewarded with a leaner operational model, where compliance and routine operations are seamlessly integrated, leading to a reduction in overall administrative costs.
- Strengthened trust and reputation
Reputation and trust are invaluable assets in today’s highly competitive market. Continuous audit readiness establishes a culture of integrity and accountability that resonates with various stakeholders, including customers, investors, and regulatory bodies.- Stakeholder Confidence: Demonstrable evidence of ongoing compliance practices reassures investors that the business is managed with a high standard of governance and operational excellence. Proof of continuous readiness can be instrumental during market valuations and financial audits, especially under frameworks like SOX.
- Customer Loyalty: Maintaining high standards of data protection and privacy – as outlined in frameworks like PCI-DSS or HIPAA – enhances customer confidence, which can translate into long-term brand loyalty.
- Competitive Advantage: A company known for its consistent adherence to multiple frameworks positions itself as a leader in corporate governance. This reputation can serve as a differentiator in markets where consumers are increasingly valuing the security and reliability of products and services.
By infusing continuous audit readiness into the corporate culture, leaders can secure an enviable reputation for responsible management, thereby attracting new opportunities for growth and partnership.
- Agile adaptability to regulatory landscape changes
The regulatory environment is in a state of constant flux. Laws such as GDPR, HIPAA, and other regional or industry-specific regulations may change frequently, creating challenges for compliance. Leaders benefit from an agile compliance model that continuously adapts to these changes. For example:- Real-Time Updates: Continuous auditing systems often integrate directly with regulatory databases, ensuring that the latest requirements are immediately reflected in compliance procedures. This agility is critical in minimizing delays in compliance adjustments.
- Scenario Planning: Businesses can run simulations to assess the potential impact of proposed regulatory changes, thereby preparing proactive strategies well in advance.
- Cross-Framework Applicability: A unified compliance management platform can support multiple frameworks simultaneously, allowing organizations to meet the diverse demands of international markets.
Through continuous audit readiness, leaders are better equipped to navigate unforeseeable regulatory challenges in an agile and efficient manner, safeguarding the company’s interests in a rapidly shifting legal environment.
Read the “Integrating control graphs for holistic risk management” article to learn more about risk management!
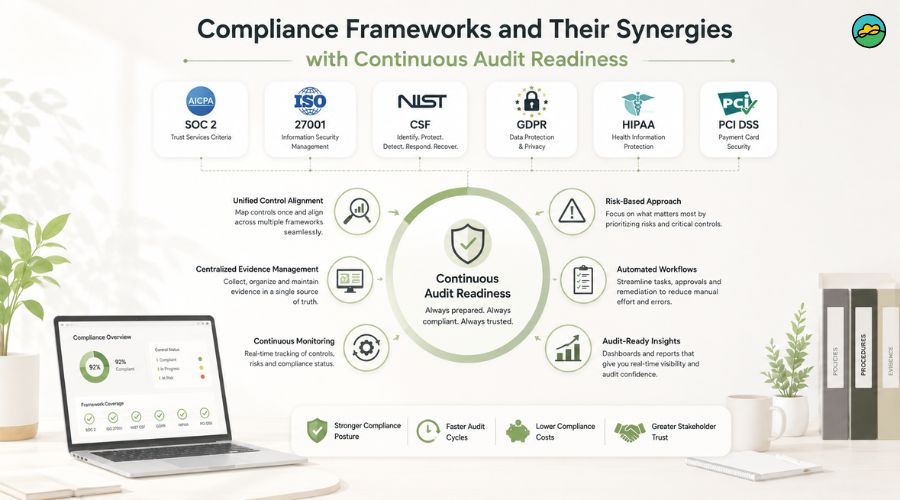
Compliance frameworks and their synergies with continuous audit readiness
A key advantage of continuous audit readiness is its compatibility with several widely recognized compliance frameworks. Leadership must understand how these frameworks interlink with continuous processes to create a robust compliance ecosystem.
SOX (Sarbanes-Oxley Act)
SOX originally targeted public companies with stringent financial record-keeping and reporting standards. Continuous audit readiness allows companies to fulfill SOX requirements consistently. Some benefits include
- Internal Control Monitoring: Real-time monitoring of internal controls ensures that deviations are identified immediately, protecting against financial misstatements and fraud.
- Enhanced Financial Reporting: Continuous validation of compliance controls improves the accuracy and reliability of financial statements, a crucial element for investor trust.
Adopting continuous audit readiness is vital for organizations seeking to mitigate financial and reputational risks tied to compliance failures under SOX.
ISO Standards (ISO 27001, ISO 9001, etc.)
The ISO family of standards promotes best practices in various operational areas, from data security (ISO 27001) to quality management (ISO 9001). Continuous audit readiness complements these frameworks by
- Routine Compliance Verification: Automated monitoring systems regularly check that operational practices meet ISO standards, ensuring ongoing compliance.
- Risk-Based Approach: Continuous audits reinforce a proactive risk management posture, identifying vulnerabilities before they impact product quality or data security.
Incorporating ISO standards into a continuous audit routine provides business leaders with an assurance of operational integrity and long-term competitive advantage.
HIPAA (Health Insurance Portability and Accountability Act)
For organizations handling sensitive patient information, complying with HIPAA’s stringent data protection norms is critical. Continuous audit readiness ensures:
- Robust Data Security: Ongoing monitoring validates that data protection measures remain effective, protecting sensitive information from breaches.
- Compliance Documentation: Continuously maintained documentation can simplify the audit process and ensure compliance with HIPAA regulations.
- Patient Trust: By demonstrating constant vigilance, organizations can uphold patient confidentiality and reinforce stakeholder confidence.
PCI-DSS (Payment Card Industry Data Security Standard)
Payment security is another critical compliance area. Continuous audit readiness supports PCI-DSS compliance by:
- Real-Time Security Posture: Monitoring payment systems continuously helps identify vulnerabilities that might be exploited, thereby preventing potential breaches.
- Audit Trail Maintenance: Automated logging and documentation facilitate smoother audits and risk management interventions.
GDPR (General Data Protection Regulation)
Operating in or with entities in the European Union necessitates adherence to GDPR, which governs data privacy and protection. Continuous audit readiness aids GDPR compliance by:
- Data Management: Continuous monitoring ensures that personal data is processed and stored in alignment with GDPR requirements.
- Incident Response: Automated alerts enable a quick response to potential data breaches, reducing the risk of non-compliance penalties.
Leaders who comprehend the interplay between continuous audit readiness and these various frameworks are well-positioned to build an integrated compliance ecology, one that is responsive and dynamic across the entire business landscape.
Read the “Use TrustCloud to accelerate NIST 800-171 readiness and self-attest” article to learn more!
Practical examples and case studies
Examining real-life examples further elucidates the tangible benefits of continuous audit readiness. Consider the following case studies that highlight success stories across various industries and compliance frameworks.
Case study 1: Financial services and SOX compliance
A multinational financial institution faced recurrent challenges in meeting the strict requirements of SOX. Traditional audit methodologies resulted in prolonged audit cycles and delayed remediation, thereby straining resources and heightening the risk of compliance breaches. By integrating a continuous audit readiness system, the institution experienced a transformation in its internal controls:
- Automated controls monitoring: The institution implemented a dedicated software solution that continuously monitored key financial transactions and flagging deviations from expected patterns.
- Proactive issue resolution: Detected issues were addressed immediately. This proactive intervention led to a decrease in audit findings during external reviews and significantly reduced the preparation effort required for annual audits.
- Cost savings: The institution reported a reduction of 30% in compliance-related costs over several fiscal years, attributing these savings to enhanced resource efficiency and early issue detection.
This example demonstrates how continuous audit readiness not only streamlines SOX compliance but also supports overall financial health by reducing waste and increasing operational agility.
Case study 2: Healthcare organization and HIPAA enforcement
A leading healthcare organization, managing extensive patient data, was challenged with the complex requirements of HIPAA. The organization’s traditional, manual auditing system was unable to keep pace with the rapid changes in health data processing and storage procedures. Transitioning to a continuous audit readiness platform delivered several benefits:
- Real-time data protection: Continuous monitoring of systems led to real-time identification and remediation of vulnerability gaps, ensuring patient data was consistently protected.
- Regulatory transparency: Automated audit trails provided comprehensive documentation during regulatory audits, thereby reducing the compliance burden on the administrative side.
- Enhanced patient confidence: With improved data security and reduced breach risk, the organization was able to strengthen its reputation among patients and regulatory agencies alike.
This case exemplifies the critical role of continuous audit readiness in balancing regulatory compliance with operational efficiency, especially in industries where data protection is paramount.
Case study 3: Retail and PCI-DSS compliance
A global retail company, processing millions of transactions daily, recognized that traditional periodic audits were insufficient to safeguard against evolving security threats. By embracing continuous audit readiness, the retailer was able to:
- Implement continuous security checks: The system continuously monitored the integrity of payment systems, automatically flagging suspicious activities related to credit card transactions.
- Maintain comprehensive logs: Automated log management, a critical requirement under PCI-DSS, was maintained consistently, easing the burden of traditional audits.
- Minimize financial risk: The retailer reduced its financial risk exposure by identifying and mitigating vulnerabilities before they could be exploited by malicious actors.
This case study highlights how a proactive approach to audit readiness can deeply integrate with the existing security infrastructure, thereby creating a safer transaction environment and improving the overall brand reputation.
Key operational goals for leaders adopting continuous audit readiness
Business leaders interested in operational excellence can extract significant strategic value from continuous audit readiness.
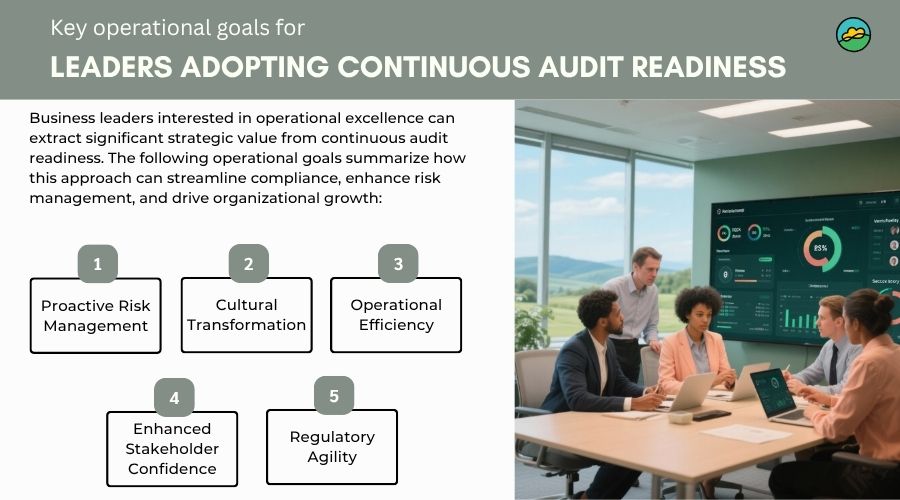
The following operational goals summarize how this approach can streamline compliance, enhance risk management, and drive organizational growth:
- Proactive Risk Management
Leaders should aim to detect potential compliance and security issues before they mature into significant risks. Establishing real-time monitoring systems that integrate with various operational processes is essential to achieving this goal. - Cultural Transformation
Embedding a culture of compliance throughout the organization is crucial. This involves incentivizing cross-departmental accountability, training staff for rapid response, and aligning the company’s strategic objectives with continuous assurance initiatives. - Operational Efficiency
Optimizing resource allocation by automating repetitive tasks can free up valuable human capital for more strategic functions. Continuous audit readiness systems help streamline operations and reduce backlogs associated with periodic reviews. - Enhanced Stakeholder Confidence
Transparent and continuous compliance processes provide confidence to investors, customers, and regulatory bodies. This improved trust can lead to better market positioning and more favorable terms during financial analysis and audits. - Regulatory Agility
Finally, by integrating advanced monitoring tools and regularly updating procedures in line with evolving regulatory standards, leaders can ensure that the organization is agile enough to adapt to changes in the business and legal environment.
HYBRID DATA FABRIC
100+ integrations to power evidence collection and real-time risk analysis
API-based integrations map seamlessly to your frameworks and controls to power automated evidence collection, continuous monitoring, and predictive risk analysis.
Strategies for implementing continuous audit readiness
Transitioning to a model of continuous audit readiness involves an organization-wide effort that leverages technology, changes processes, and enhances organizational culture.
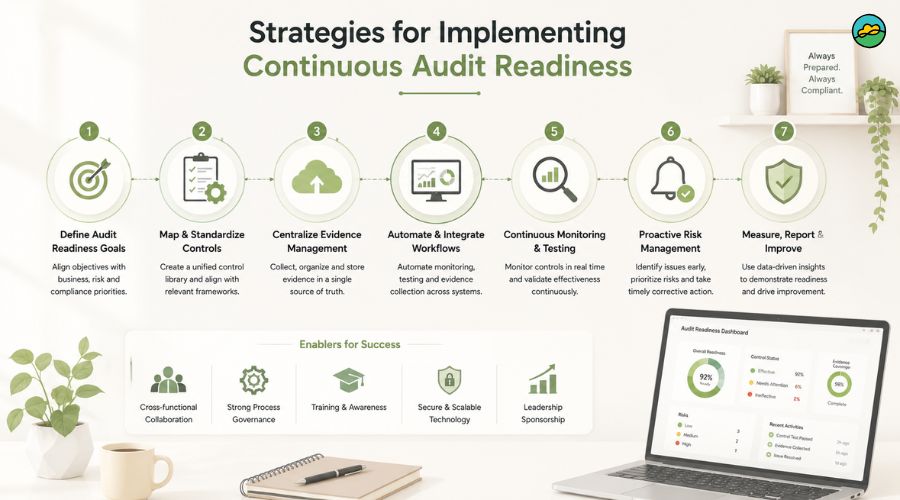
Leadership can adopt the following strategies to implement this transformative approach:
- Invest in advanced technology
Modern audit readiness relies heavily on the integration of automated monitoring tools and data analytics platforms. Leaders should consider investing in:- Audit Management Software: Platforms that can automate compliance checks and continuously capture relevant data are integral to maintaining readiness.
- Data Analytics Tools: Real-time data analysis not only identifies non-compliance early but also provides insights into operational trends, enabling proactive strategy adjustments.
- Cloud-Based Solutions: As organizations embrace cloud infrastructures, it is critical to implement cloud-based auditing tools that integrate seamlessly with existing frameworks and provide instant alerts for anomalous activities.
- Enhance employee training and culture
A culture of continuous audit readiness starts with employees. Leaders should:- Conduct Regular Training: Empower staff by providing targeted training sessions on compliance-related responsibilities and the use of new auditing technologies. Reinforce the idea that every employee plays a role in the organization’s compliance framework.
- Promote Accountability: Develop clear lines of accountability across all departments. Highlight the role of each function in maintaining the overall state of readiness and reward proactive behavior.
- Foster a Compliance-First Mindset: Create internal communications and incentives that underscore the importance of continuous improvement, not just for compliance but as a driver of business excellence.
- Integrate compliance frameworks into business processes
Leaders must ensure that continuous audit readiness is not viewed as a separate function but rather as an integral component of daily operations.- Process Mapping: Conduct a comprehensive review of existing operational processes to identify integration points where compliance checks can be embedded.
- Cross-Functional Collaboration: Encourage departments such as IT, legal, and operations to work closely together toward a unified compliance strategy.
- Regular Reviews and Updates: Establish a routine for periodic reviews of compliance processes to ensure they are up-to-date with industry best practices and emerging regulatory requirements.
- Leverage data for strategic decision-making.
One of the most significant benefits of continuous audit readiness is the wealth of data it generates. Business leaders should aim to- Conduct Trend Analysis: Utilize historical audit data to discern patterns and predict future compliance challenges. This analytical insight supports proactive decision-making and resource allocation.
- Implement Dashboards: Develop executive dashboards that provide real-time visibility into compliance statuses across various business functions. These dashboards can be integrated with financial, operational, and risk management insights for a comprehensive view.
- Drive Business Strategy: Let the insights generated from continuous audits feed into broader corporate strategies, ensuring that compliance insights are used as a catalyst for improving overall operational efficiency and competitive positioning.
TrustCloud delivers multi-framework readiness out-of-the-box
TrustCloud automates continuous audit readiness across SOX, ISO 27001, HIPAA, PCI-DSS, and GDPR by mapping controls into one dashboard; no more framework silos eating your time. API-tested evidence is collected automatically from cloud configs, endpoints, and apps, flagging drifts instantly via ML-powered alerts. Sales teams share live Trust Portals proving real-time compliance, cutting questionnaire hell by 90%. A fintech cut SOX prep from 12 weeks to 3 days; healthcare firms passed HIPAA unannounced audits seamlessly. Boards track unified KPIs, risk scores are down 40%, and costs are slashed 30%, turning audits from a drag to a dashboard demo.
Leadership wins big: scenario planning simulates reg changes pre-impact, cross-framework synergies spot gaps early (e.g., GDPR data flows feeding SOX financials). No-code workflows embed testing into CI/CD, devs fix vulns before deploy, and ops monitor 24/7. Scale from startup to enterprise; free trials prove ROI in weeks. Customers report 50% faster deals and zero surprise findings. Continuous readiness isn’t future-proofing; it’s today’s edge, where compliance fuels agility, not anchors it down. Integrate once, audit forever across stacks. (98 words)
Summing it up
Achieving and maintaining compliance across frameworks like ISO, HIPAA, SOC 2, or CMMC doesn’t have to be a reactive scramble. With continuous audit readiness, you’re building a foundation of trust, operational efficiency, and strategic insight. By integrating control alignment, automated evidence collection, and real-time monitoring into one unified system, you eliminate the cycle of last-minute prep and firefighting, empowering your team to focus on meaningful improvements instead.
This proactive posture translates into clear business value: faster audit cycles, reduced compliance costs, and elevated confidence among clients, regulators, and leadership. Continuous readiness isn’t a checkbox; it’s how modern organizations embed resilience into daily operations. With readiness that never sleeps, audits become smoother, risks shrink, and compliance evolves into a strategic advantage, strengthening both your security posture and your bottom line.
Frequently asked questions
What is continuous audit readiness, and why does it matter?
Continuous audit readiness refers to an always-on state where an organization’s compliance posture is maintained in real time. Instead of preparing documents only ahead of audits, this approach uses automated tools to collect evidence, monitor controls, and generate reports continuously.
The benefit? Your team never scrambles for data at audit time. Because controls and evidence are tracked consistently, audit preparation becomes far easier and less disruptive. This method offers greater transparency, faster issue detection, and reduces the risk of non-compliance.
For businesses managing multiple standards like SOC 2, ISO 27001, or GDPR, continuous audit readiness ensures you’re always compliant across all relevant frameworks—without duplicating effort each time.
How does continuous control assurance support audit preparedness?
Continuous control assurance (CCA) underpins audit readiness by actively measuring and testing control performance across systems. Rather than yearly or quarterly spot checks, CCA uses automated monitoring and analytics to detect anomalies or control failings as they happen.
This proactive model helps identify issues early – such as missed password expirations, policy exceptions, or misconfigured access – and allows you to fix them before auditors raise red flags. It also generates audit trails automatically, keeping records of control status over time.
With such audit-grade documentation, you can reduce time spent on manual checks, avoid penalties, and foster a culture of continuous compliance improvement.
What are the financial benefits of adopting continuous audit readiness?
Though implementing continuous audit systems requires an upfront investment in tools and training, it yields significant long-term savings. First, audit preparation costs decline dramatically—there’s less manual labor, fewer remediation cycles, and fewer consultant fees. Second, early detection of control gaps prevents fines and operational disruptions tied to compliance breaches.
Third, with readily available audit-ready data, the auditing process is faster, often reducing audit fees. Finally, operational efficiency improves—processes run more smoothly, issues are resolved before they escalate, and reporting becomes second nature. In short, continuous readiness shifts compliance from reactive fire‑fighting to proactive business assurance.
How does continuous audit readiness benefit business operations?
Adopting continuous audit readiness offers several operational advantages. It streamlines compliance processes, reducing the time and resources spent preparing for audits. This efficiency leads to cost savings and allows teams to focus on core business activities. Additionally, by maintaining up-to-date compliance measures, organizations can quickly adapt to regulatory changes, minimizing disruptions.
Continuous readiness also fosters a culture of accountability and transparency, which can improve internal processes and decision-making. Overall, it enhances operational agility, enabling businesses to respond swiftly to new challenges and opportunities.
What challenges do organizations face without continuous audit readiness?
Organizations that do not maintain continuous audit readiness often encounter several challenges. They may face increased risk of non-compliance due to outdated controls or missed regulatory updates, leading to potential fines and reputational damage. The lack of preparedness can result in rushed, inefficient audit processes, consuming valuable time and resources. Additionally, these organizations may struggle to demonstrate their commitment to security and compliance to clients and partners, potentially losing business opportunities. Without continuous readiness, businesses are less equipped to navigate the complexities of modern regulatory environments, hindering their growth and competitiveness.
Why is continuous readiness valuable for multiple frameworks?
Continuous readiness is valuable across multiple frameworks because many compliance requirements overlap. If an organization manages controls in a fragmented way, teams often duplicate work, maintain separate records, and spend unnecessary time proving the same thing in different formats. The article highlights that a unified readiness model allows organizations to map controls once and use them across several frameworks, which reduces waste and improves consistency. That makes compliance more efficient and easier to sustain as obligations grow.
It also helps organizations avoid confusion when different frameworks have similar but not identical requirements. A continuous approach makes it easier to track how a single control supports multiple obligations and where additional work is needed. This is especially important for companies operating in regulated industries or across geographies. Instead of building one-off processes for every audit, they can create a stronger underlying compliance system that supports scale, resilience, and faster audit cycles.
How does continuous audit readiness improve risk management?
Continuous audit readiness improves risk management by helping teams identify and address issues earlier. The article emphasizes real-time visibility, which means teams can spot anomalies, control failures, or compliance gaps as they happen rather than discovering them late in a formal review. That earlier detection gives organizations a better chance to fix problems before they expand into larger security, legal, or operational risks. It also helps leaders understand where the biggest exposures are and prioritize their efforts accordingly.
This proactive model also shortens remediation timelines. When evidence, controls, and reporting are already being maintained throughout the year, there is less delay between finding an issue and correcting it. That reduces the likelihood of regulatory penalties, failed audits, or business disruption. In practice, continuous readiness turns risk management into a live process rather than an annual exercise, which is much more effective for modern organizations facing fast-changing threats and regulatory expectations.
How does this approach reduce costs?
The article presents continuous audit readiness as a way to lower costs by reducing the manual effort and disruption associated with traditional audit preparation. When audit readiness is maintained continuously, teams do not need to pause normal work for last-minute evidence gathering, urgent policy updates, or repeated coordination across departments. That reduces labor costs and avoids the inefficiency of “big-bang” audit preparation. It also allows organizations to use their time and resources more strategically.
Cost savings also come from fewer compliance failures and faster remediation. If issues are caught early, the organization is less likely to face expensive fines, rework, or legal consequences. Automation can further reduce administrative overhead by streamlining routine tasks like evidence collection and status tracking. Over time, these efficiencies can significantly reduce the total cost of maintaining compliance across multiple frameworks. The article makes the point that readiness is not just a defensive expense; it can be a practical way to operate leaner and smarter.
How does it improve operational efficiency?
Continuous audit readiness improves operational efficiency by integrating compliance work into normal business processes instead of treating it as a separate burden. The article describes how automation, standardized workflows, and real-time reporting reduce repetitive manual tasks and limit duplicated effort. This means teams spend less time chasing documents or fixing inconsistencies and more time on high-value work. It also reduces the fatigue that often comes with periodic audit cycles, where employees are pulled away from their regular responsibilities to prepare evidence under pressure.
Another efficiency gain comes from better collaboration. When compliance information is centralized and continuously updated, different teams can work from the same source of truth. That makes communication easier and reduces mistakes caused by outdated spreadsheets or scattered records. As a result, the organization becomes more organized and more responsive. In practical terms, continuous readiness helps teams move faster while maintaining stronger control over compliance quality.
How does it strengthen stakeholder trust?
Continuous audit readiness strengthens stakeholder trust because it shows that the organization takes governance and accountability seriously. The article notes that clients, partners, investors, and regulators are more confident in a business that can demonstrate ongoing compliance rather than last-minute preparation. When a company can show that controls are monitored regularly and evidence is kept current, it signals discipline and maturity. That can be especially important in sales cycles, procurement reviews, or investor discussions where trust is a deciding factor.
Trust also grows because the organization appears more transparent and reliable. Stakeholders want to know that risks are being managed consistently, not just during formal review periods. A continuous readiness posture helps reassure them that the business is not improvising when scrutiny appears. Over time, that can support stronger relationships, faster approvals, and a better reputation in the market. The article frames this as a competitive advantage, not just a compliance benefit.
What role does automation play in continuous readiness?
Automation is one of the foundations of continuous audit readiness. The article explains that automated workflows can collect evidence, track control status, send reminders, and create real-time reports without relying entirely on manual effort. This is important because manual processes are hard to scale and easy to miss. Automation helps ensure that the readiness process is consistent and always active, which is exactly what continuous readiness requires.
Automation also makes cross-framework management more practical. A unified platform can map one control to multiple requirements and keep the evidence current across frameworks. That reduces duplication and makes reporting more efficient. It also supports faster remediation because issues are surfaced sooner and with clearer context. In short, automation turns continuous readiness from an ambitious idea into an operational reality that teams can sustain year-round.
