

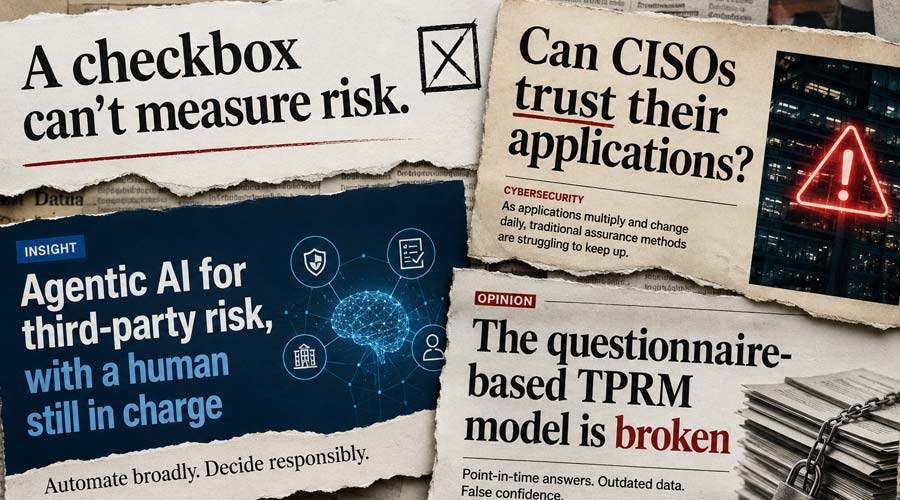
Independent journalists, analysts, and working CISOs are all reaching the same conclusion about questionnaire-based, point-in-time risk assessment: it’s no longer enough.
Risk and vulnerabilities keep growing, compliance obligations keep stacking up, and AI adds an entirely new surface to account for. CISOs need something better: a continuous approach with visibility across their business, that actually reduces risk rather than just documenting it.
Over the past two months, journalists, a McKinsey partner, an industry analyst, and working CISOs have each said it in their own words. Below is the coverage, and what each piece means if you’re the one who has to stand in front of a board and vouch for your risk posture.
Dark Reading: a checkbox can’t measure risk
Dark Reading’s feature brings together several experts all pointing to the same flaw in once-a-year, checkbox compliance. As McKinsey partner Lamont Atkins put it, a vendor can be fully compliant on paper and still introduce real risk into your business.
A CISO has to translate technical risk into a picture leadership can act on, but a static annual attestation makes that harder, because it describes a moment that has already passed.
The piece also captures a point from TrustCloud CEO Sravish Sridhar that reframes what trust actually means: trust isn’t the absence of problems. You will have breaches, anomalies, and bad days; what matters is whether you can see them and respond. By that logic, a tool that constantly reports good news may be the one to worry about, because it probably isn’t catching what it should.
SecurityWeek: Can CISOs trust their applications?
For many CISOs, judging whether their applications can be trusted still comes down to a manual process that takes weeks and, in practice, often happens only once a year. By the time the picture is assembled, it’s already out of date.
That’s the practice Application Assurance is built to replace: continuous, AI-driven monitoring of the data around an application, so a CISO can see current risk and emerging risk on demand rather than reconstructing it from a survey. SecurityWeek’s Kevin Townsend framed it as bringing an archaic practice into the age of managed automation.
MSSP Alert: agentic AI for third-party risk, with a human still in charge
Vendor security risk is a high-priority for most CISOs, and TrustLens is built to help. The platform lets teams assess more vendors, review evidence faster, and keep monitoring for changes after the assessment closes, eliminating time-consuming and questionnaire-heavy assessments.
With a “people-led” approach, the TrustLens agent automates more than 70% of the assessment work, leaving final decisions and approvals with the risk analyst. That’s the right division of labor for CISOs, compliance leaders, and MSSPs: the AI does the heavy lifting and surfaces what you need, and a human still makes the call.
Help Net Security: the questionnaire-based TPRM model is broken
The numbers in this one make the case on their own. Using TrustLens, one customer assessed more than 5,000 suppliers in six months, a 10x improvement, and surfaced 4x more critical gaps than its previous process had. Each assessment can be scoped to the individual vendor rather than sent as a one-size-fits-all form. This cuts the burden on the people answering and gives the assessing team real-time insight into a vendor’s profile, risks, and gaps without the endless back-and-forth of chasing responses.
Read the Help Net Security piece
Help Net Security: new infosec products of the month
TrustLens also made Help Net Security’s notable products list for May 2026, alongside a number of established names. As a category, the shift away from the security questionnaire is gaining momentum.
See the Help Net Security May 2026 roundup
Where this leaves us
The common thread across all five pieces: risk is continuous, so assurance has to be continuous too. That’s the premise behind TrustLens, which replaces manual, point-in-time questionnaires with data-driven, API-native assessments that keep watching controls and any changes long after the box is checked.
The market is now saying it out loud. The honest question for most CISOs is no longer whether the annual questionnaire is enough, it’s how much longer they’re willing to rely on it. If your GRC program still starts and ends with a form, it may be worth seeing what continuous assurance actually looks like.
A few questions CISOs are asking
Why is questionnaire-based TPRM considered broken?
Because a questionnaire captures a single moment. It records what a vendor said on one day, not whether the controls are real, working, or still in place months later. Risk keeps moving; the questionnaire doesn’t.
What is replacing point-in-time vendor assessments?
Continuous, data-driven assessment. It draws on live evidence and outside-in signals, keeps watching for drift after the assessment closes, and sizes each review to the vendor’s actual risk rather than sending everyone the same form.
Does AI make the risk decisions?
No. AI handles the heavy lifting, scoping, evidence review, and summaries, while the risk analyst keeps the final call. Every analysis is meant to be explainable, cited, and auditable.
How does continuous monitoring help with board reporting?
It lets you present current, evidence-backed risk on demand instead of defending a snapshot from last quarter, and turn technical findings into something the board can act on.
What is vendor security drift?
It’s the gap that opens between an assessment and reality, when a vendor’s posture, subprocessors, or configurations change after they passed your review. Continuous monitoring is what catches it.
