

One Unexpected SOC 2 Challenge: Overcoming Cultural Resistance to Security-First Thinking
When companies start their SOC 2 journey, most expect the technical checklist: configure access controls, deploy logging, and gather evidence. But what we’ve consistently seen with our customers is that the toughest part isn’t the technology. It’s the culture.
SOC 2 compliance is often framed as a technical or operational milestone. But after guiding multiple organizations through the SOC 2 implementation process, I can confidently say that one of the most unexpected and arguably most complex challenges is cultural: shifting an entire organization’s mindset to embrace a “security-first” ethos.
While technical controls, documentation, and third-party audits are crucial, they are not the steepest hills to climb. What most organizations fail to anticipate is how deeply human behavior, organizational habits, and departmental silos can obstruct progress. Security is not a siloed function; it must be integrated into daily workflows, decision-making, and company values. And changing behavior at scale is never easy.
Read the “Confidently choose your SOC 2 trust service criteria” article to learn more!
This article explores that unexpected challenge in detail, offering insights, lessons learned, and tactical strategies for any team preparing for their own SOC 2 journey.
Key takeaway
What we’ve learned is simple: Tools make compliance easier. Culture makes it real. The companies that succeed don’t just pass the audit; they build a foundation where every team owns a piece of security. That’s the part no checklist prepares you for. And that’s the part that makes all the difference.
Beyond the checklist, why SOC 2 is harder than it looks
At first glance, SOC 2 seems straightforward: gather evidence, document policies, and adopt the right tools to meet the Trust Services Criteria. Many leadership teams start here, treating compliance like a technical to-do list. But anyone who’s gone through a readiness project knows the reality is far more complicated. SOC 2 isn’t just about servers, logs, or access controls; it’s about how people work, make decisions, and interact with security in their day-to-day roles.
The hardest part of SOC 2 isn’t the frameworks or the auditors; it’s the cultural shift it demands. Engineers may resist extra steps that slow down velocity, sales teams may see security reviews as blockers, and managers may underestimate the importance of documentation. Left unchecked, these cultural gaps can derail timelines, create inconsistent evidence, and leave your company scrambling during audits.
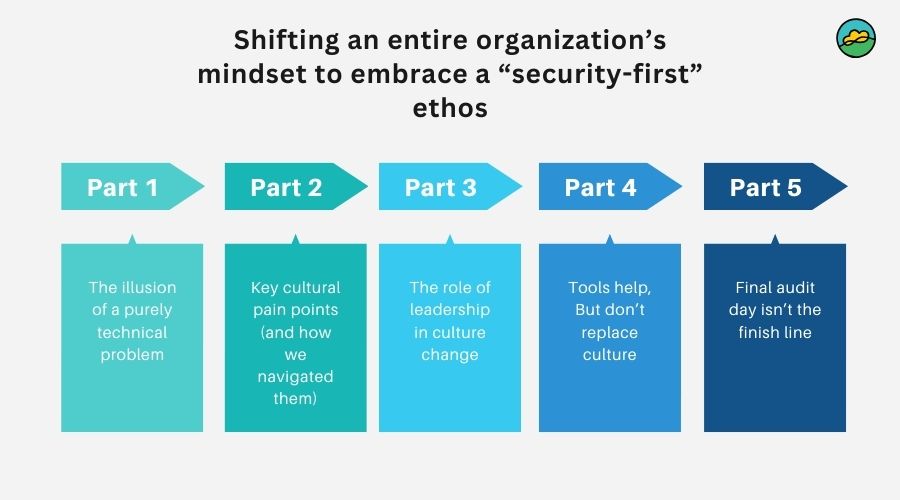
The following guide shares what we learned navigating SOC 2 from the inside. You’ll see why treating compliance as “just a technical exercise” is the first and most dangerous, miscalculation, and how building a security-first culture is the real foundation for long-term success.
Part 1: The illusion of a purely technical problem
When leadership teams kick off their SOC 2 preparation, there’s usually an initial focus on systems and processes:
- What evidence do we need to collect?
- What policies must be documented?
- What tools should we implement for logging, monitoring, or access control?
These are all valid questions, but they imply that SOC 2 is a technical exercise. That’s the first major miscalculation.
SOC 2 isn’t just a test of your infrastructure. It’s an evaluation of how securely your organization operates, and that includes people. According to a report by Verizon, 74% of data breaches involve the human element, whether it’s error, misuse, or social engineering. 【source: Verizon 2023 Data Breach Investigations Report】. SOC 2 recognizes this, which is why the Trust Services Criteria include not just system operations, but also risk management, personnel onboarding, and access governance.
The Cultural Gap
Despite these requirements, companies often overlook the degree to which their team culture may clash with SOC 2 principles:
- Engineers are focused on velocity, not documentation.
- Product teams prioritize user experience, not secure defaults.
- Customer-facing roles may perceive security reviews as bottlenecks to sales.
The outcome? Even with the right tools and frameworks in place, friction emerges when people don’t understand why security matters or how it should be integrated into their work. This friction can delay audits, create inconsistent evidence, and lead to non-conformities during assessments.
Part 2: Key cultural pain points (and how we navigated them)
Lack of cross-functional alignment
In our first SOC 2 readiness project, we made the mistake of keeping the initiative “within security and compliance.” The result? Weeks of delays waiting for evidence from engineering, stale documentation, and confusion around responsibilities.
What we learned: Every department plays a role in SOC 2. Success required creating a RACI matrix (Responsible, Accountable, Consulted, Informed) that clearly outlined ownership for every control.
What we did:
- Created department-specific training for product, HR, engineering, and sales.
- Held monthly cross-functional syncs to track progress and unblock dependencies.
- Used collaborative tooling like TrustCloud to assign tasks and collect audit-ready evidence automatically.
Engineering pushback on “Security debt”
Engineers, by nature, thrive in systems that reward speed, iteration, and problem-solving. SOC 2, by contrast, rewards consistency, auditability, and control.
Initially, when we asked teams to implement controls like
- MFA enforcement across all accounts
- Logging changes in GitHub
- Access reviews every quarter
…we were met with resistance. “This slows us down,” or “We’ll do it later” became common refrains.
Our turning point came when we reframed SOC 2 not as a restriction, but as an enabler of trust with customers, with partners, and even with regulators. We also brought engineers into the design of the control implementation so they could choose how to meet the requirements, giving them autonomy within constraints.
Documentation apathy
SOC 2 demands policies, dozens of them. Everything from onboarding checklists to incident response plans to change management procedures. But getting people to follow and update these documents regularly? That’s the real challenge.
In one company, we found that only 30% of managers had reviewed the acceptable use policy with their teams, even though they had “acknowledged” it in a system like Confluence.
To address this, we:
- Integrated policy reviews into onboarding and quarterly refreshers.
- Used simple quizzes post-review to ensure comprehension.
- Adopted document management tools that tracked not just acknowledgments but engagement.

Looking for automated, always-on IT control assurance?
TrustCloud keeps your compliance audit-ready so you never miss a beat.
Learn MorePart 3: The role of leadership in culture change
One of the biggest success factors in our journey was executive sponsorship. When the CEO and CTO started including “security updates” in company all-hands, it signaled that this wasn’t just a checkbox; it was part of our DNA.
Leaders can accelerate culture change by:
- Publicly recognizing teams who implement good security practices.
- Holding directors accountable for their role in control effectiveness.
- Being transparent about security incidents or audit gaps (in appropriate forums).
This top-down advocacy helped transform security from “someone else’s problem” to “everyone’s job.”
Part 4: Tools help, But don’t replace culture
Tools like TrustCloud, Drata, Vanta, or Secureframe automate evidence collection, policy management, and risk registers. They are incredibly helpful in maintaining continuous compliance. But tools cannot enforce a security culture.
We saw this firsthand when a team toggled off a critical logging feature; technically, it wasn’t caught until the next quarterly check. The lesson? You need both automation and awareness.
To strengthen the human element, we:
- Built a lightweight “Security Champions” program where each team nominated one person to stay in sync with security policies and updates.
- Ran phishing simulations and gamified results (e.g., prizes for teams with the fewest click-throughs).
- Conducted “brown bag” sessions on real-world security breaches and what we could learn from them.
Part 5: Final audit day isn’t the finish line
Another unexpected challenge was the post-certification complacency. After months of effort, when we finally got the SOC 2 Type II report, teams assumed the hard part was over.
In reality, SOC 2 requires ongoing evidence collection. Many controls must be repeated periodically (e.g., quarterly access reviews, annual risk assessments). If your culture hasn’t internalized this, the next audit period becomes a fire drill all over again.
To prevent that:
- We embedded control check-ins into regular team workflows.
- Used TrustCloud to maintain a “control calendar” and send reminders.
- Measured maturity over time, e.g., how quickly teams closed security tickets, updated access, or logged incidents.
The goal wasn’t just to pass the audit but to operate like a SOC 2-compliant company every single day.
Sustaining a security-first culture after your first SOC 2
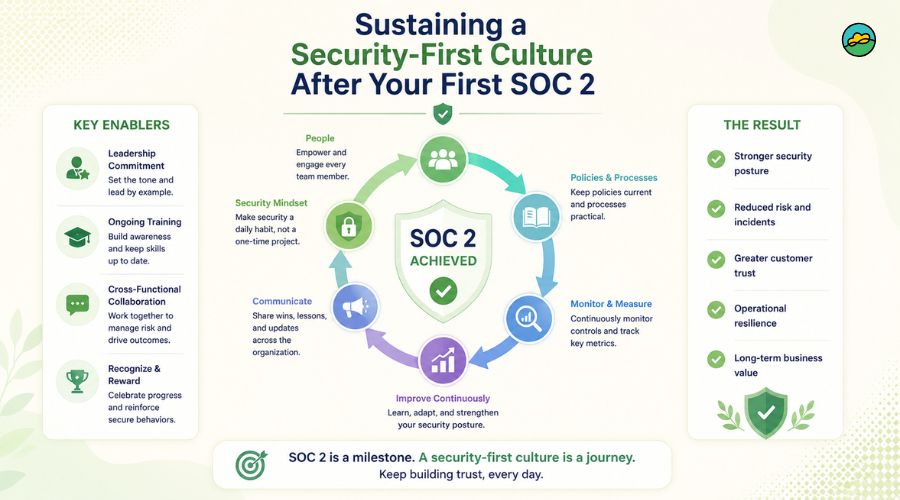
The cultural shift required for SOC 2 doesn’t end once you’ve earned your report; in many ways, that’s when the real work begins. To avoid slipping back into old habits, organizations need simple, repeatable ways to keep security-first thinking visible in everyday work, so controls don’t feel like a special project but part of how the company naturally operates.
Embed security topics into recurring forums like sprint reviews, product councils, and all-hands meetings, so discussions about controls, risks, and incidents stay routine instead of exceptional.
Maintain a lightweight “security champions” network across teams who can translate SOC 2 expectations into team-specific practices and spot cultural friction early.
Tie elements of SOC 2 behavior, like timely access reviews, incident reporting, or clean audit trails, to performance goals or team OKRs to reinforce that security outcomes matter.
Regularly refresh training with real internal examples and customer stories to show how strong security practices prevented issues or helped close deals, not just to satisfy a checkbox.
Use pulse surveys and retrospectives after key compliance milestones to learn where processes felt painful or confusing, then improve them before the next audit period.
When you intentionally maintain this cultural momentum, SOC 2 becomes less about surviving each audit window and more about building a trusted, resilient organization. Over time, teams begin to see security not as a constraint on innovation but as a shared advantage that protects their work, strengthens customer relationships, and makes every future audit easier than the last.
Turning SOC 2 into a company-wide operating mindset
One of the most overlooked realities of SOC 2 implementation is that compliance cannot succeed as a siloed initiative owned exclusively by security or compliance teams. Organizations often begin their SOC 2 journey assuming the process is primarily technical, centered around access controls, logging systems, evidence collection, and policy documentation. While those elements are critical, the real challenge emerges when security expectations begin affecting everyday workflows across engineering, HR, operations, sales, and leadership teams.
Employees who are focused on product velocity, customer acquisition, or operational efficiency may initially view compliance requirements as obstacles rather than business enablers. This disconnect can create friction, delayed evidence gathering, inconsistent policy adoption, and resistance to operational changes. Successful organizations overcome this challenge by transforming SOC 2 from a “project” into an operational mindset embedded throughout the company. Cross-functional accountability, executive sponsorship, and ongoing communication become essential for creating alignment. When teams understand how security directly supports customer trust, enterprise sales, and long-term business resilience, compliance efforts become more collaborative and sustainable instead of reactive and burdensome.
Another important challenge organizations frequently underestimate is maintaining consistency after initial readiness efforts begin. Many businesses successfully implement controls during the early stages of SOC 2 preparation but struggle to operationalize them over time.
Documentation becomes outdated, quarterly reviews get postponed, onboarding procedures vary across departments, and manual evidence collection creates operational fatigue. This is especially difficult for fast-growing companies where systems, teams, and infrastructure evolve rapidly. As organizations scale, maintaining audit-ready processes manually becomes increasingly inefficient and error-prone. Modern compliance platforms and automation tools are helping organizations address this issue by introducing continuous control monitoring, automated evidence collection, centralized policy management, and real-time compliance visibility. Instead of scrambling before an audit period, businesses can maintain an ongoing state of readiness while reducing administrative overhead. More importantly, automation allows organizations to integrate compliance into everyday workflows, helping teams sustain operational discipline without slowing innovation or growth.
Companies that adopt continuous compliance models often experience stronger governance, improved risk visibility, and greater confidence during audits and customer security reviews.
Perhaps the most transformative shift during SOC 2 implementation occurs when organizations realize that compliance maturity directly influences strategic business outcomes. Enterprise customers increasingly expect vendors to demonstrate not only technical security controls but also operational reliability, governance maturity, and long-term accountability. SOC 2 therefore becomes more than a regulatory requirement; it evolves into a trust-building mechanism that can accelerate sales cycles, strengthen customer relationships, and improve competitive positioning. Organizations that align SOC 2 initiatives with broader business objectives gain significantly more value from the process. Leadership teams can use compliance insights to improve operational resilience, streamline vendor management, strengthen incident response readiness, and support strategic planning decisions.
This alignment also helps shift employee perception away from “checklist compliance” toward a culture of ownership and accountability. Over time, companies that successfully embed SOC 2 principles into their daily operations develop stronger security habits, better decision-making frameworks, and more sustainable governance practices. In an environment where trust and transparency increasingly influence purchasing decisions, turning SOC 2 into an operational discipline rather than a temporary certification effort can become a lasting business advantage.
Summary: What to expect and how to prepare
Here are the main takeaways for any organization preparing for SOC 2:
✅ Don’t treat SOC 2 as just a technical exercise.
Security is as much about people as it is about systems. The audit evaluates how your company operates, not just your codebase.
✅ Expect resistance from teams not used to security rigor.
Engineers, product managers, and even executives may view compliance as a burden unless you show how it builds customer trust.
✅ Get cross-functional alignment early.
Establish responsibilities, timelines, and training plans that include every relevant department; security can’t do it alone.
✅ Automate where possible, but reinforce with culture.
Tools reduce human error, but you still need champions, education, and feedback loops to keep the culture alive.
✅ Treat your first SOC 2 report as the beginning, not the end.
Build systems for continuous compliance so your teams are never caught off guard during the next audit period.
The unexpected challenge of SOC 2 isn’t technology; it’s transformation. Shifting your organization’s culture to prioritize security in every decision is hard, messy, and rarely discussed. But once that shift happens, something remarkable follows: security becomes a strength, not a speed bump. Customers notice, teams take pride, and your company becomes not just compliant but trusted.
And that, ultimately, is the true goal of SOC 2.
FAQs
What’s the most unexpected challenge organizations face when implementing SOC 2?
One surprising hurdle that many organizations encounter is mis-scoping the SOC 2 audit, from over-scoping to under-scoping. Striking the right balance is tougher than it looks. Go too narrow, and you risk omitting critical systems or data paths tied to customer commitments; too broad, and you burden your team with unnecessary work and audit noise. Misjudging scope can result in misallocated resources, extended timelines, and even audit failure. The key is to carefully map every system touching customer data and then validate that inventory with stakeholders and your auditor. That way, scope becomes strategic, not an afterthought.
Why is managing third-party and vendor risk so difficult during SOC 2 readiness?
Many organizations don’t anticipate how intertwined their systems are with vendors, service providers, and partners, yet every external connection introduces a potential compliance blind spot. The real challenge is not only identifying which vendors matter for SOC 2 but also collecting up-to-date assurance from them and continuously tracking their security posture. If one vendor isn’t compliant or fails to manage risk properly, it could ripple into your own audit. The solution is creating a structured vendor assessment pipeline: assess, document, monitor and loop in remediation where needed to shore up the weakest links.
Why does evidence collection and organization often become a compliance breaking point?
Evidence is the lifeblood of SOC 2 audits and yet it’s often the most chaotic, overlooked component. Auditors want proof of more than just policies; they expect logs, monitoring dashboards, access reviews, incident histories, and more, all formatted clearly and paired with control objectives. When evidence is scattered across emails, spreadsheets, or local drives, you lose credibility fast. Manual collection eats time and invites mistakes. The smarter route is to centralize documentation early, use automated tools where possible, and align evidence directly with control mappings. That way, you build audit readiness into your daily operations, not just scramble when the audit window opens.
Why is cross-functional alignment essential for a successful SOC 2 program?
Cross-functional alignment is essential because SOC 2 touches almost every part of the organization, not just security or IT. Engineering owns many technical controls, product influences secure defaults and data flows, HR manages onboarding and offboarding, and sales and customer success handle security questionnaires and customer commitments. If these teams are not aligned on priorities, timelines, and responsibilities, you end up with duplicated work, missing evidence, and misunderstood expectations.
For example, security may assume engineering is running quarterly access reviews, while engineering assumes security is doing it. A clear RACI (Responsible, Accountable, Consulted, Informed) matrix, regular cross-functional check-ins, and role-specific training ensure everyone understands what SOC 2 requires from them. This alignment turns SOC 2 from a siloed initiative into a coordinated company effort, reducing surprises close to audit time and making continuous compliance more realistic.
Why aren’t tools alone enough to solve SOC 2 challenges?
Tools can automate evidence collection, centralize documentation, and streamline control monitoring, but they cannot replace human judgment, behavior, and accountability. A platform may show whether MFA is enabled, logs are flowing, and tickets are being closed, yet it can’t decide if teams understand why these controls matter or if they will keep them enabled under pressure. Tools also depend on accurate configuration and ongoing use; a feature toggled off or a process skipped can create unseen gaps that only surface at audit time.
Without a strong culture, people may treat tools as a box-checking exercise, uploading bare-minimum artifacts or working around controls for convenience. When culture comes first, through education, shared responsibility, and leadership support, tools become powerful force multipliers that make good behaviors easier and more consistent. Together, culture and tooling create a sustainable, always-on compliance posture; on their own, tools simply mask deeper issues.
How should organizations think about SOC 2 after receiving their first report?
After receiving their first SOC 2 report, organizations should treat it as the starting point of a new operating model rather than the end of a project. The report proves that controls were in place and effective over a defined period, but future audit windows will expect the same or higher level of rigor. Controls such as quarterly access reviews, annual risk assessments, incident response exercises, and policy updates need to continue on a defined cadence. If teams relax and return to pre-audit habits, the next period will involve another frantic scramble, and auditors may find gaps in consistency.
Instead, organizations should embed control activities into existing workflows, maintain a living control calendar, and track metrics like time-to-complete reviews or close security tickets. By normalizing SOC 2 tasks as business-as-usual and continuously learning from each cycle, companies evolve from “getting compliant” to truly operating as a trusted, security-first organization.
