

Imagine landing a big SaaS deal, only for the prospect to pause and think about privacy compliance: “Show us your GDPR and CCPA proofs alongside SOC 2, oh, and ISO 27701 mappings too.” Suddenly, scattered spreadsheets and siloed audits turn a slam dunk into weeks of scramble. Privacy regs multiply like rabbits, €20M GDPR fines grab headlines, and CCPA class actions hit millions, while ISO 27701 and SOC 2 privacy criteria demand ironclad data flows. Teams drown chasing compliance theater, burning cash on consultants instead of closing sales. Sound familiar? The fix isn’t more paperwork; it’s unified proof that scales.
TrustCloud flips the script with Privacy Essentials, baking GDPR, CCPA, ISO 27701, and SOC 2 privacy into one dashboard. Auto-map existing controls, generate new ones via API-tested evidence, or craft customs for your quirks, no more reg-by-reg whack-a-mole. Prospects peek at your Trust Portal for real-time reports, auditors sign off faster, and boards track risk drops quarterly. Customers slash audit time 50%, win deals 40% quicker, and sleep knowing privacy powers growth, not gridlock. Ready to turn obligations into your edge?
Your challenge
Keeping track of all your privacy and security obligations can be expensive, time-consuming, and challenging! Every time you think you’ve got a handle on one regulation, several more pop up on your radar. You want to do the right thing by making sure that you have the right policies and controls in place, but you don’t have the time or resources to sort through the nuances and complexity involved in trying to meet the requirements for GDPR, CCPA, ISO 27701, and SOC 2’s privacy criteria.
There’s no need to be in the depths of despair…we’ve got just the solution for you!
How we solved your challenge
We know that privacy is important to you, so we’ve crafted a few features in TrustOps to help you implement a privacy program in your organization. You have the option of bringing in your existing privacy programs and automating them or auto-generating one from scratch in TrustOps.
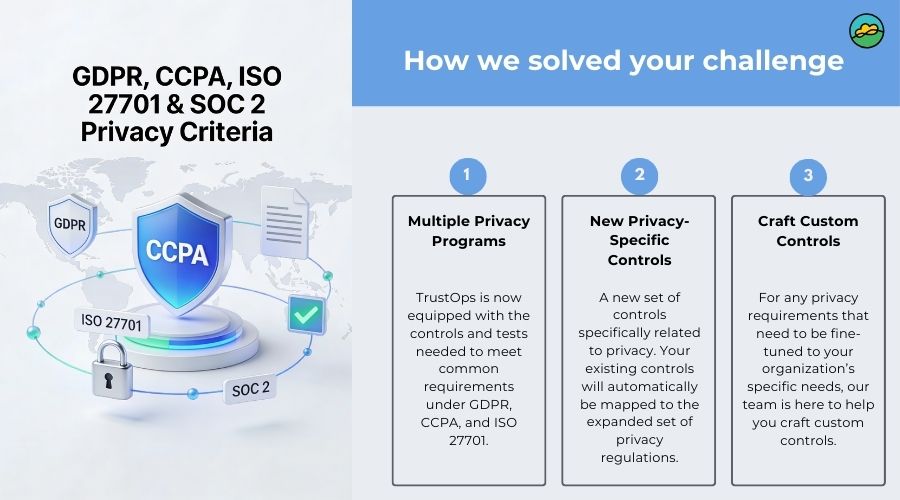
Multiple Privacy Programs: TrustOps is now equipped with the controls and tests needed to meet common requirements under GDPR, CCPA, and ISO 27701.
New Privacy-Specific Controls: TrustOps now has a new set of controls specifically related to privacy. Your existing controls will automatically be mapped to the expanded set of privacy regulations.
Craft Custom Controls: For any privacy requirements that need to be fine-tuned to your organization’s specific needs, our team is here to help you craft custom controls.
TrustCloud unifies GDPR, CCPA, ISO 27701, and SOC 2 privacy
TrustCloud tackles the sprawl of privacy regs head-on by mapping controls across GDPR, CCPA, ISO 27701, and SOC 2 privacy criteria in one dashboard. Bring your existing programs or auto-generate new ones, TrustOps handles the heavy lifting with API-tested evidence, custom controls for unique needs, and automatic mappings that save weeks of manual work. No more siloed spreadsheets; track data flows, consent tracking, and breach workflows seamlessly, proving compliance to auditors and customers alike. Teams report 50% faster audits, turning privacy from headache to competitive edge.
Real value hits when you impress prospects with a Trust Portal, questionnaire-free sharing of SOC 2 reports, ISO 27701 artifacts, and GDPR/CCPA gap analyses. Continuous monitoring flags drifts instantly, while preferred partner pricing bundles pen tests and audits. Boards love KPI dashboards showing risk scores dropping quarter-over-quarter. Customers in SaaS, healthcare, and fintech shave compliance costs by 40%, focusing on growth instead of regs. Privacy Essentials is a verifiable trust that accelerates deals and builds lasting relationships. (198 words)
The value to you
With the addition of key privacy regulations in TrustOps, you will realize the following benefits:
- You have access to a single platform to track, measure, and mitigate security and privacy risks since all controls, policies, and evidence are automatically mapped to the multiple standards, certifications, and regulations
- You now have the ability to meet the common requirements for multiple privacy regulations simultaneously
- You will save time, effort, and resources with built-in workflow automation tools
- You will build trust with your customers by implementing verifiable data privacy policies and controls that are tested via APIs, and facilitating truthful communication about privacy practices with individuals, business partners, assessors, and regulators
Our approach
At TrustCloud, our mission is to make it effortless to earn trust in every business relationship. We fundamentally believe in operating with complete transparency and openness. By publishing our product roadmap and sharing new feature updates, we hold ourselves accountable to you and continue to prove that we deliver on our commitments.
Our beliefs shine through to our product development methodology, where new features are developed based on lessons from numerous customer interactions and interviews, and early versions are vetted with design partners. When we release a feature to your instance, we want you to be able to tell that we poured ourselves into it, that we’ve joyfully crafted TrustCloud just for you.
Unified privacy governance
A strong privacy program today is no longer built around a single regulation. Most organizations operate across multiple jurisdictions, serve customers with different expectations, and collect data through a mix of product, marketing, and support workflows, which means GDPR, CCPA, ISO 27701, and SOC 2 privacy controls often need to work together. A useful section for this article would explain that the real challenge is not passing each framework separately, but creating one privacy operating model that can satisfy them all without duplicating effort. That framing makes the article more practical for readers who are trying to scale compliance as the business grows.
The value of a unified privacy model is that it creates consistency in how organizations define data handling, privacy requests, retention, consent, and third-party oversight. Instead of maintaining separate policies and evidence packs for each framework, teams can build a common control layer and map it to the specific requirements of each standard. This helps reduce confusion, lowers the chance of conflicting answers during audits or customer reviews, and makes privacy governance easier to maintain over time. It also positions privacy as a business capability, not just a legal obligation.
Privacy maturity is increasingly tied to trust and market access. Customers, regulators, and partners want to see that privacy is managed continuously, not reactively. By showing how GDPR, CCPA, ISO 27701, and SOC 2 privacy requirements overlap and reinforce one another, the article can help readers understand that a harmonized approach supports faster sales cycles, smoother compliance operations, and stronger resilience. That makes the section relevant for both compliance leaders and business stakeholders.
Interested in exploring how Privacy Essentials can help you? Schedule a meeting here.
