

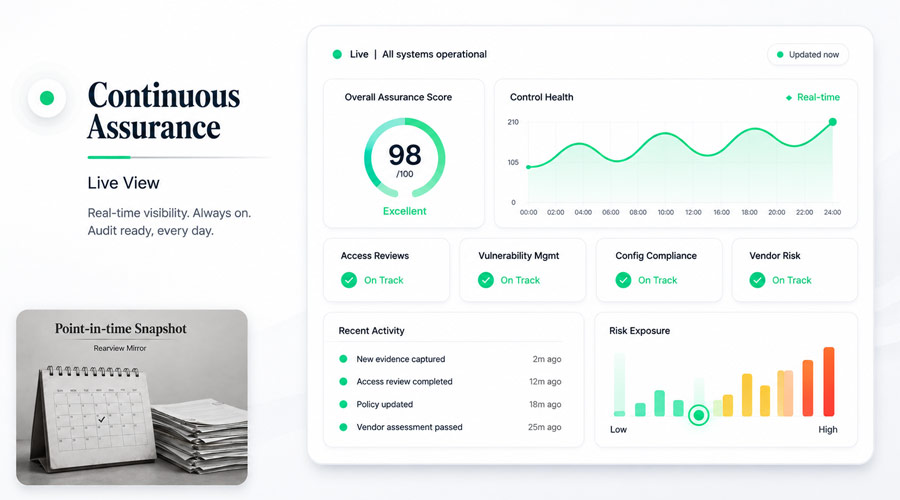
Enterprise security teams need to secure a risk surface that is constantly changing. However, the tools in their stack were built to check only a fraction of that risk. For confirmation, they rely on static snapshots and annual attestations. I now see this as the defining problem in GRC.
When 451 Research (S&P Global) initiated coverage of TrustCloud in this space, they described a clear and growing divide. The old GRC model was built for periodic, workflow-driven compliance, but that approach no longer serves modern enterprise needs or risks. In fact, many enterprises have left legacy GRC tech in search of a solution that delivers continuous visibility into risk and compliance posture.
We need a fundamentally different approach. At TrustCloud, we’ve taken to calling it cyber risk assurance: continuous, evidence-based proof that a business is operating securely, across both first- and third-party risk. It is a discipline the whole industry is moving toward, not merely a product feature.
Cyber risk assurance rests on three capabilities that legacy GRC was never built to deliver.
Continuous control monitoring, not point-in-time snapshots
AI governance mandates and data privacy rules have piled on new areas to monitor, expanding faster than most teams can staff for. In the 451 Research Voice of the Enterprise: Data & Analytics, Data Governance & Privacy 2026 survey, nearly half of respondents named the complexity of regulations and law as a cultural barrier to managing data privacy. That figure matches what I see in the field. Most teams are working hard against this, but legacy tools cause structural roadblocks, because a calendar-based process cannot keep pace with mandates for real-time visibility into controls.
Continuous control monitoring is the first requirement of cyber risk assurance. Instead of sampling controls on a schedule, it collects evidence through direct API connections to the systems those controls run on, and maps each control to that evidence in the Control Graph. Assurance reflects the state of the business today rather than its state at the last audit.
Third-party risk needs continuous visibility, not annual questionnaires
The clearest example is third-party risk. In the 2025 Verizon Data Breach Investigations Report, the share of breaches involving an external partner doubled in a single year, from 15% to 30%. An annual questionnaire will not catch a vendor’s security posture drifting between assessments. That blind spot is a serious source of exposure for enterprises with large vendor ecosystems.
Cyber risk assurance has to cover the full vendor ecosystem, on the same platform and the same data model as internal controls, monitored continuously through APIs rather than reconstructed from email threads once a year. Vendor risk should be observed as it changes, not attested once and filed away.
Board reporting that ranks risk by business impact to drive decisions
Gartner reports that 93% of board members agree cyber-risk threatens shareholder value. Many CISOs now present updates directly to their boards. However, the way security is positioned in those updates has largely stayed the same. Most CISOs still report in the vocabulary of security functions when their boards are asking business questions. Their GRC tools were built to report compliance status, so the responsibility to translate dashboards into board-level language falls back on the CISO.
This is what makes cyber risk assurance credible in the boardroom: findings ranked by business impact with a clear evidence trail. The AI has to be designed to leave that trail. Ours runs on small language models that operate only from cited, structured evidence and are scored against a governance framework aligned with ISO 42001 and the NIST AI Risk Management Framework. Every figure it surfaces traces back to the evidence behind it, which is exactly what a board needs for confident decision-making.
Where enterprise security is heading
Resilient security programs no longer see GRC as looking ‘in the rearview mirror’ at events of the past. They treat it as a live view on whether the business can operate safely. Cyber risk assurance is the standard enterprise programs will require for a more resilient future. Those teams will be able to report real business impact to their leadership rather than audit completion alone.
If you want the outside perspective on where this is heading, 451 Research (S&P Global) assessed the case for continuous cyber risk assurance in their recent coverage of TrustCloud.
