

Continuous control monitoring may sound like a program you have to rebuild your whole GRC function to reach. It isn’t. It’s a phased build that integrates with the systems you already run, and a focused team can have continuous monitoring live across its priority controls in about a month.
This guide explains how: what the 30-day path looks like, what to turn on first, and what “done” actually means at the end of the first month. It goes a step past the fundamentals, assuming you already know that continuous control monitoring tests your controls automatically against live data rather than by hand once a year, and why that beats point-in-time audits. To get that foundation, start with our companion piece on why CISOs should prioritize continuous control monitoring in 2026.
How do you implement continuous control monitoring?
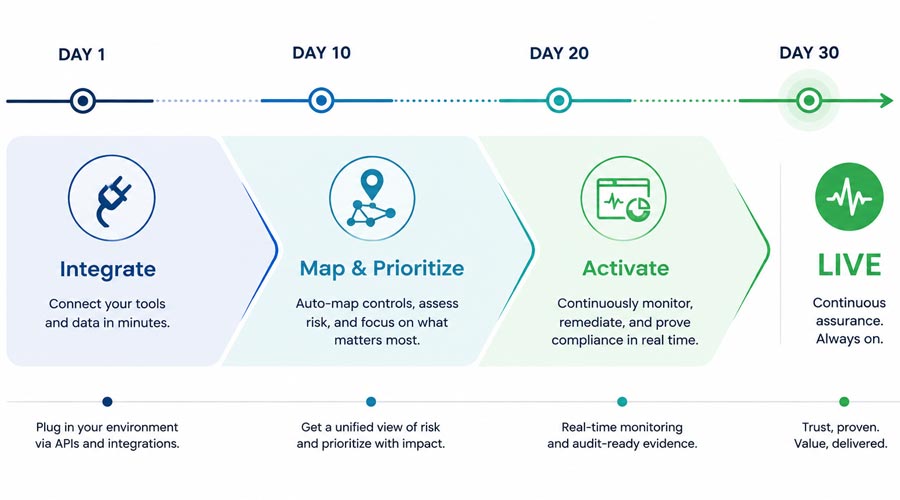
You implement it in three phases over 30 days: connect your systems, map and prioritize your controls, then switch on live monitoring and reporting. The sequence is key. Each phase depends on the one before it, and trying to monitor controls you haven’t mapped, or map controls from data you haven’t connected, is where most stalled projects go wrong.
Here’s what each phase covers.
Days 1 to 10: integrate your tech stack and APIs
Start by connecting the systems that hold the evidence. Continuous monitoring only works if it can read the real state of your environment, so the first job is wiring in your cloud platforms, infrastructure, identity providers, ticketing, and the other systems of record where control activity actually happens.
The goal for these first ten days is to see clean, continuous data flowing in from across your stack. This is where TrustCloud works with your existing investments rather than around them: it integrates directly with the operational tools you already run and feeds continuous control data into them, making your existing stack more useful, not redundant. The platform reads evidence from those systems through APIs to become the source of truth your monitoring layer sits on top of.

Tejas Ranade
Chief Product Officer, TrustCloud
“The time and cost required to get full visibility manually are prohibitively high. Automation is the only solution.”
Days 11 to 20: map controls and prioritize risk to your framework
With data flowing, the next ten days are about structure. Map your controls to a framework scoped to your actual regulatory and business obligations, whether that’s SOC 2, ISO 27001, GDPR, NIST, or a combination, and establish clear relationships between risks, policies, applications, and the compliance standards they answer to.
This is also where you prioritize, since not every control carries the same weight. Sequence the work by connecting each control to what its failure would actually affect: a contract, a customer commitment, a regulatory obligation, a critical application. The controls tied to mission-critical business move to the front of the queue. This points your monitoring where a failure would cost the most, rather than spreading it evenly across every signal. In TrustCloud, the Control Graph makes this possible, mapping each control to the policies, applications, risks, and commitments it covers so those connections are already in place when you set your order of work.
Days 21 to 30: activate real-time monitoring and dashboards
In the final phase, you switch monitoring on. Automated tests run continuously against the controls you mapped using the data flows you connected, and reporting dashboards show what’s working, what’s failing, and what needs attention.
By day 30 you have a live system. Controls are tested automatically, gaps get flagged as they appear rather than at audit time, and you can report in a way your team and your leadership can understand and use to make informed decisions. Your static picture is now continuous.
What do you monitor first?
Start with your highest-impact controls on your most critical applications, not everything at once. You’ll quickly lose momentum if you try to monitor your entire environment on day one.
Remember these guiding principles:
- Aggregate and cut the noise. Pull data from your diverse systems and focus on the signals that point to real, actionable risk rather than drowning the team in alerts.
- Lead with critical assets. Prioritize the applications, infrastructure, and data that carry the most business, financial, or regulatory weight.
- Automate the repetitive checks first. Control validations you currently do by hand, like access reviews, are the ones that pay off fastest when automated, freeing the team for higher-priority work.
- Give every metric business context. Tie what you monitor back to organizational objectives so the output speaks to leadership, not just to the security team.
Not sure which dashboards to stand up first? The CISOs’ Guide: Automate Security, Privacy, and AI Risk Assessments lays out the full set and where to start.
How long does it take to set up continuous control monitoring?
The initial build runs about 30 days across the three phases above, and coverage keeps growing from there as you extend monitoring across more of your environment.
You can see the timeline in a Fortune 100 technology company: first findings surfaced within 30 days, and within 90 days it had automated 24 controls across 12 data feeds, giving its CISO a defensible, industry-benchmarked view of residual risk. A Fortune 100 pharmaceutical company shows where that leads: continuous monitoring of its crown-jewel applications scaled from roughly 20% under manual questionnaires to 96%, replacing point-in-time surveys with real-time, evidence-backed assurance.
So the 30 days gets you a working system, not the finish line. The payoff grows with coverage, including audit readiness that turns a multi-week internal audit into a short confirmation.
What does high-confidence assurance look like at day 30?
At the end of the first month, you’ve moved from checking controls by hand on a fixed schedule to watching them continuously with live data. Gaps show up when they happen. Reporting reflects the current state, not last quarter’s. And the manual effort that used to eat your team’s time is redirected to the risks that actually need human judgment.
That’s the real payoff. Continuous control monitoring isn’t a bigger version of the annual audit. It’s a different posture: always-on assurance that you can take to an auditor, a customer, or your board with confidence, built on the systems you already run.
Ready to go deeper to automate your full risk-assessment program?
Read the 2026 CISOs’ Guide to Automate Security, Privacy, and AI Risk Assessments.
FAQ
Is continuous control monitoring the same as continuous monitoring?
“Continuous monitoring” is often used loosely to mean security operations or infrastructure monitoring. Continuous control monitoring specifically means testing your compliance and security controls on an ongoing basis, so the “control” part is what distinguishes it.
Do you have to replace your existing GRC tools to implement continuous control monitoring?
No. Continuous control monitoring integrates with the operational systems you already run and reads evidence from them through APIs. You’re adding an assurance layer on top of your existing stack, not tearing out and rebuilding your environment.
What controls should you automate first?
Start with the highest-impact controls on your most critical applications, and prioritize the repetitive manual checks, like access reviews, that pay off fastest when automated. Expanding coverage from that core is more sustainable than trying to monitor everything at once.
Can you really implement continuous control monitoring in 30 days?
Yes, for the initial build. A focused, phased approach (integrate, map and prioritize, activate) stands up a working system in about a month, and coverage expands from there.
What frameworks does continuous control monitoring support?
It maps to the frameworks your obligations require, including SOC 2, ISO 27001, GDPR, and NIST, often several at once. Mapping controls to a tailored framework is the second phase of the build.
