


Defense contractors and suppliers working with the Department of Defense (DoD) are under increasing scrutiny to prove that their cybersecurity controls meet strict requirements. The Cybersecurity Maturity Model Certification (CMMC) is now a non-negotiable benchmark that organizations must meet to remain eligible for defense contracts. But reaching CMMC compliance is not just about checking boxes; it’s about demonstrating sustained, verifiable cybersecurity practices that align with national security priorities.
This is where AI-powered platforms are proving indispensable. Instead of relying on manual tracking, spreadsheets, and fragmented workflows, these systems can automate evidence collection, identify control gaps, and maintain continuous monitoring. AI doesn’t replace human oversight; it enhances it. It flags risks early, surfaces audit-ready documentation, and keeps your team aligned with evolving CMMC levels.
The advantage is speed and scale. As CMMC requirements grow more rigorous, AI enables organizations to stay agile and compliant without stretching internal resources thin. For leaders navigating this space, adopting AI tools isn’t just about compliance; it’s about resilience and long-term competitiveness. Integrating smart technology into your compliance strategy now will pay dividends as requirements evolve and enforcement tightens across the defense supply chain.
What is CMMC?
CMMC (Cybersecurity Maturity Model Certification) is a standardized framework designed to ensure that companies in the Defense Industrial Base (DIB) meet specific cybersecurity practices when handling controlled unclassified information (CUI) for the U.S. Department of Defense (DoD). It provides a structured approach to protecting sensitive defense-related data across contractors and subcontractors.
CMMC is organized into maturity levels, ranging from Level 1 (basic cyber hygiene) to Level 5 (advanced/progressive cybersecurity practices). Each level has a defined set of practices and processes that an organization must implement to achieve certification. The certification is mandatory for DoD contractors, and the required level depends on the type and sensitivity of the information handled.
Executive summary
The Department of Defense has set a high bar for cybersecurity across its supply chain through CMMC, which requires defense contractors to implement robust controls and continuously evolve their cyber defenses. Given the complexity and dynamism of these requirements, traditional manual methods of compliance are increasingly proving insufficient. The integration of AI-powered platforms offers a promising alternative by automating compliance monitoring, detecting potential vulnerabilities in real-time, and accelerating the overall journey to CMMC readiness.
This article explores the multifaceted benefits of using AI in the context of CMMC compliance, highlighting key challenges and presenting a set of practical, strategic recommendations for leaders. It provides clarity on how AI capabilities such as natural language processing, machine learning, and data analytics can be harnessed to not only meet but exceed compliance benchmarks. In doing so, organizations stand to achieve enhanced operational efficiency, improved cybersecurity risk management, and a robust competitive edge in a market where rapid compliance is synonymous with trust and reliability.
For executive leadership, the decision to integrate AI-powered platforms into cybersecurity strategies is driven by the need to transform reactive compliance measures into proactive, resilient, and agile organizational processes. This transformation is essential in today’s increasingly complex threat landscape, where cyber adversaries are constantly evolving tactics. The article aims to demystify AI-driven compliance solutions, providing executives with a roadmap for successful transformation and sustained excellence in defense cybersecurity.

Looking for automated, always-on IT control assurance?
TrustCloud keeps your compliance audit-ready so you never miss a beat.
Learn MoreUnderstanding CMMC and the DoD environment
The Department of Defense has long depended on trusted partners and suppliers, making cybersecurity a paramount consideration in its operations. The CMMC is designed as a unified cybersecurity standard that combines various compliance frameworks into one holistic approach. Its primary role is to ensure that organizations working on government contracts have a strong foundation in safeguarding controlled unclassified information (CUI) and other sensitive data.
Historically, many companies have struggled with the implementation and sustained maintenance of robust cybersecurity frameworks. In response, the DoD mandated a multi-level approach to CMMC that organizations must meet in order to secure their place within the defense ecosystem. This requirement, though challenging, paves the way to a more secure operational environment that can handle the dynamic nature of modern cyber threats.
The CMMC framework is composed of multiple maturity levels, each with specific requirements forecasting a measure of cybersecurity best practices. It places increasing demands on organizations, from basic cyber hygiene practices at entry-level stages to advanced practices involving proactive threat detection and incident response at higher levels. Such an evolution reflects both the growing sophistication of cyber threats and the overarching goal to protect national security interests.
Read the “Automating evidence collection for regulatory compliance: Tools & best practices” article to learn more!
The rise of AI in cybersecurity
Artificial intelligence is transforming industries across the spectrum, and cybersecurity is no exception. AI-driven solutions have proven to be extraordinarily helpful in detecting patterns of unscrupulous activity and reacting to them in near real time. For organizations pursuing CMMC compliance, AI has created the possibility of transforming traditionally manual tasks into efficient, automated processes.
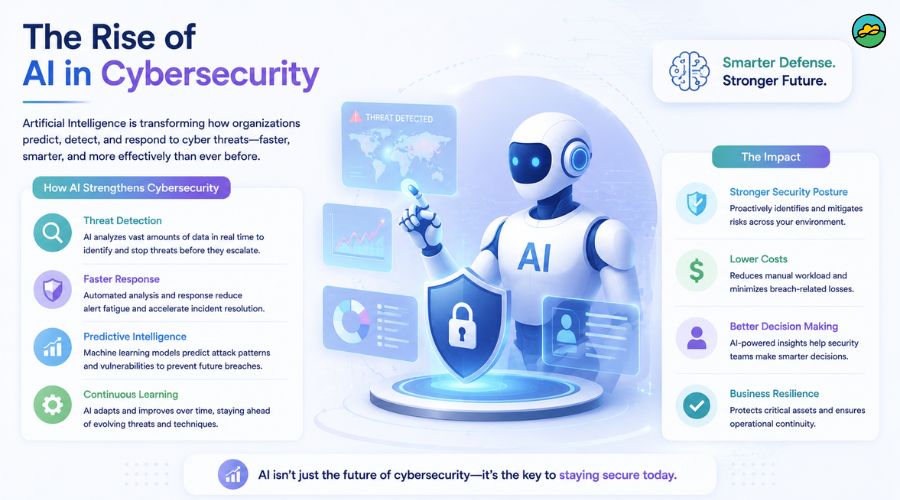
One of the key advantages of using AI in cybersecurity is its capability to monitor vast amounts of data continuously, which is essential for flagging potential security breaches before they escalate. This predictive behavior, powered by machine learning algorithms, not only reduces response times but also minimizes human error. Moreover, AI systems can learn from previous incidents, thereby refining their accuracy over time.
The implications are significant for DoD contractors tasked with meeting stringent security requirements. By integrating AI tools into their cybersecurity arsenals, organizations can identify vulnerabilities, predict emerging threats, and maintain a proactive security posture. In many cases, these tools offer scalable solutions, meaning that as an organization grows, so too does its AI-enhanced defense mechanism.
The defense industry is at a crossroads
Over the past few years, cybersecurity has transitioned from being viewed as an operational necessity to a strategic imperative that directly impacts national security and economic resilience. Historically, compliance with cybersecurity standards involved laborious manual processes, often leading to delays, inefficiencies, and elevated risk exposure. With CMMC now in the spotlight, organizations must adopt faster, smarter methods to effectively safeguard critical information and infrastructure.
Amid these challenges, AI-powered platforms have emerged as a transformative force capable of automating compliance processes, pinpointing vulnerabilities before they can be exploited, and offering continuous, real-time insights that empower decision-makers. By integrating these advanced tools with traditional cybersecurity frameworks, organizations can not only meet the requirements of the CMMC but also cultivate a culture that embraces innovation, resilience, and proactive risk management.
CMMC Overview and Guides
This guide talks about the Cybersecurity Maturity Model Certification (CMMC), a comprehensive framework launched by the Department of Defense (DoD) to protect the defense industrial base from cybersecurity threats.
Understanding CMMC and its strategic importance
CMMC is more than just a checklist of cybersecurity controls; it is an intricate framework designed to fortify the defense supply chain against increasingly sophisticated cyber threats. The model categorizes requirements into five levels, each escalating in complexity and control intensity. As organizations progress through these levels, they must demonstrate both the implementation and continuous effectiveness of their cybersecurity practices.
The strategic importance of achieving and maintaining CMMC compliance cannot be overstated. For defense contractors, compliance is the gateway to securing DoD contracts. However, beyond this immediate business necessity, stringent controls ensure that sensitive data and technologies remain protected from adversaries. This protection is crucial not only in mitigating risks of intellectual property theft or espionage but also in preserving national security interests globally.
Moreover, CMMC compliance instills confidence among stakeholders, ranging from government officials to private sector partners, by showcasing a commitment to robust cybersecurity practices. In an increasingly interconnected world, organizations that demonstrate high levels of compliance are better positioned to forge strategic partnerships, enhance reputation, and ultimately drive long-term growth.
Read the “Effortless compliance: TrustCloud boosts your CMMC Level 1 readiness” article to learn more!
Key challenges in achieving CMMC compliance
Achieving CMMC (Cybersecurity Maturity Model Certification) compliance is a critical milestone for organizations operating within the defense supply chain but it’s far from simple. The framework demands not only strong cybersecurity practices but also meticulous documentation, continuous monitoring, and cultural alignment across teams. For many organizations, balancing these requirements while managing limited resources and evolving cyber threats can be overwhelming.
From complex technical controls to navigating shifting regulatory updates, the path to certification often feels like navigating a maze. Understanding the key challenges in achieving CMMC compliance is the first step toward developing a focused, sustainable strategy that turns compliance from a burden into a competitive advantage.
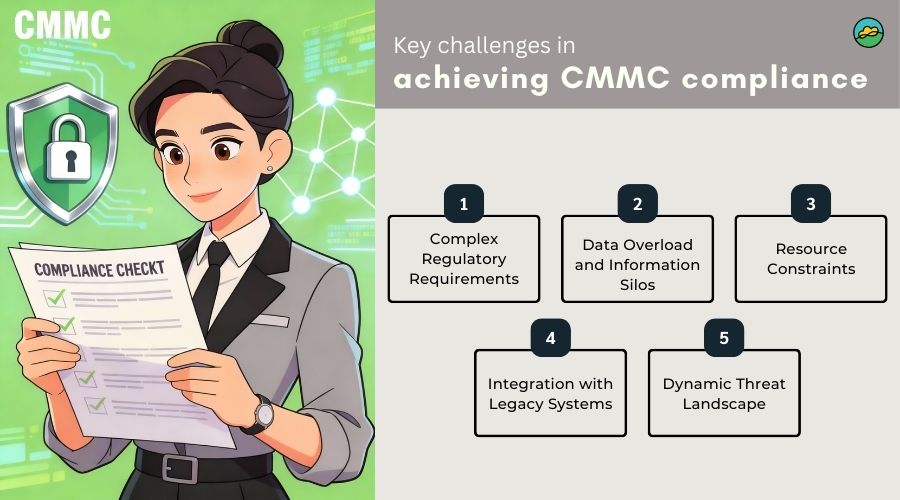
While the benefits of CMMC compliance are substantial, the path to achieving and maintaining this standard is fraught with challenges. Understanding these challenges is the first step in formulating effective strategies that leverage AI for accelerated compliance.
- Complex and Evolving Regulatory Requirements
CMMC requirements are both comprehensive and dynamic. As the threat landscape evolves, regulatory bodies continuously update and refine compliance standards. This complexity can overwhelm traditional cybersecurity teams that are already stretched thin by day-to-day operations. The constant need to interpret nuanced requirements, adapt policies, and implement new controls demands significant expertise and resources. - Data Overload and Information Silos
One of the primary challenges in managing CMMC compliance is the vast amount of data involved. Organizations accumulate large volumes of logs, alerts, and compliance reports from disparate systems, creating information silos that impede holistic analysis. Manual reviews of such massive datasets risk oversight, lead to fragmented insights, and can delay corrective actions in a timely manner. - Lack of Skilled Personnel and Resource Constraints
The cybersecurity talent gap remains a significant obstacle for many organizations. Highly skilled professionals are required to interpret complex data analytics, configure sophisticated security controls and manage compliance frameworks. However, the global shortage of cybersecurity experts means many organizations are forced to operate with lean teams, making it difficult to keep pace with evolving CMMC requirements. - Integration with Legacy Systems
Many organizations work with legacy IT infrastructures that were not originally designed to integrate with modern, automated systems. This legacy gap can hinder the deployment of AI-driven platforms, as older systems may lack the necessary APIs, data interoperability, or scalability required for real-time analytics. Integrating modern AI capabilities with existing systems often involves a significant upfront investment in both time and resources. - Dynamic Threat Landscape
The pace at which cyber threats evolve outpaces the traditional methods of compliance management. Attack vectors, malware behaviors, and intrusion tactics change rapidly, rendering static compliance processes obsolete. Organizations face the dual challenge of staying compliant with evolving regulations while simultaneously defending against a constantly shifting threat landscape. This duality pushes the need for adaptive systems that can dynamically respond to emerging threats.
Read the “Risk anticipation: scenario planning for uncertain futures” article to learn more!
AI-driven solutions: Transforming CMMC compliance
The road to achieving and maintaining CMMC compliance is notoriously complex, often burdened with manual documentation, time-consuming audits, and ever-changing cybersecurity requirements. However, the rise of Artificial Intelligence (AI) is reshaping this landscape entirely. By bringing speed, accuracy, and intelligent automation into compliance workflows, AI transforms what was once a reactive process into a proactive, data-driven strategy. Instead of struggling to keep up with evolving Defense Department mandates, organizations can now leverage AI to predict risks, automate control mapping, and ensure continuous readiness.
Artificial Intelligence offers a revolutionary approach to overcoming many of the challenges described above. Its inherent ability to process vast amounts of data, learn from patterns, and adapt in real time makes AI an ideal partner in the quest for CMMC compliance. Below are the core AI-powered strategies that can transform compliance processes within the defense industry.
- Automated Data Analysis and Continuous Monitoring
AI-powered platforms excel at data ingestion and analysis. By leveraging algorithms that sift through logs, network traffic, and system alerts, these platforms can continuously monitor environments for anomalies or deviations from established compliance baselines. Machine learning models can identify patterns in large datasets that might indicate potential vulnerabilities or attempted breaches. This real-time analysis not only speeds up the identification of risks but also ensures that organizations remain compliant even as new threats emerge. For example, a continuous monitoring system driven by AI can map activities across the network and flag any behavior that deviates from defined acceptable patterns. This early-warning capability enables swift remediation actions, reducing the window of opportunity for attackers and enhancing overall security posture. - Streamlined Documentation and Reporting
Documenting compliance is a resource-intensive process that often involves manual data collection and report generation. AI-driven automation simplifies this process by integrating with existing systems to automatically generate compliance reports. Natural language processing (NLP) capabilities can transform technical data into comprehensible narratives that serve multiple stakeholders, from technical teams to executive boards.
This streamlined reporting process is particularly valuable for meeting the audit requirements of CMMC. Automated documentation not only reduces the risk of human error but also enables organizations to quickly compile evidence of compliance, significantly accelerating audit readiness. By centralizing data from various sources, AI systems can produce comprehensive compliance reports that detail control implementations, incident response times, and corrective actions taken over time. - Predictive Analytics and Threat Intelligence Integration
AI-driven predictive analytics can significantly enhance an organization’s ability to forecast emerging threats and anticipate areas of non-compliance before they manifest as security incidents. By integrating threat intelligence feeds with internal monitoring data, AI platforms can predict potential vulnerabilities and proactively suggest mitigation strategies. This forward-looking approach allows organizations to be one step ahead of adversaries, aligning with the proactive security culture required for DoD compliance. Predictive analytics also support resource planning and budgeting by forecasting the potential impact of various threat scenarios, thereby enabling organizations to strategically prioritize their investments in cybersecurity measures. This predictive capability reduces the likelihood of compliance lapses and enhances overall organizational resilience. - Enhanced Identity and Access Management (IAM)
Identity and access management is a critical component of CMMC. AI technologies can augment traditional IAM systems by continuously learning user behavior patterns, identifying deviations from normal access habits, and automating responses to suspicious activities. Such dynamic IAM systems ensure that only authorized users have access to sensitive data, aligning directly with the requirements of controlled access mandated by the CMMC framework. Moreover, AI can integrate biometric data and advanced authentication methods to provide a layered security approach that minimizes risk. By continuously adapting to user behavior, AI-powered IAM solutions can reduce the likelihood of insider threats, unauthorized access, and other security breaches. - Intelligent Incident Response and Remediation
The speed at which an organization can detect a security incident and remediate it directly influences its overall risk posture. AI-powered incident response platforms can automatically correlate alerts from various sources, triage events based on severity, and trigger predefined remediation workflows. By automating these processes, organizations can drastically reduce the time required to neutralize threats and prevent escalation.
Integrating AI with Security Information and Event Management (SIEM) systems creates an ecosystem where potential incidents are not only detected in real-time but also contextualized with historical data. This enables rapid decision-making and ensures compliance with CMMC mandates for timely incident reporting and response. The outcome is a robust, self-healing infrastructure that minimizes both the frequency and impact of security breaches.
Read the “Data privacy and AI: ethical considerations and best practices” article to learn more!
Strategic recommendations for executives
When cyber threats evolve faster than traditional compliance methods can keep up, executive leadership plays a defining role in driving transformation. The integration of AI-powered platforms into CMMC compliance is a strategic evolution that demands vision, accountability, and cross-functional alignment.
Executives must view AI as both a compliance accelerator and a resilience enabler, capable of reducing risk while improving operational efficiency. By adopting a forward-looking mindset, fostering collaboration between IT, security, and compliance teams, and ensuring ongoing investment in intelligent automation, leaders can position their organizations ahead of regulatory shifts.
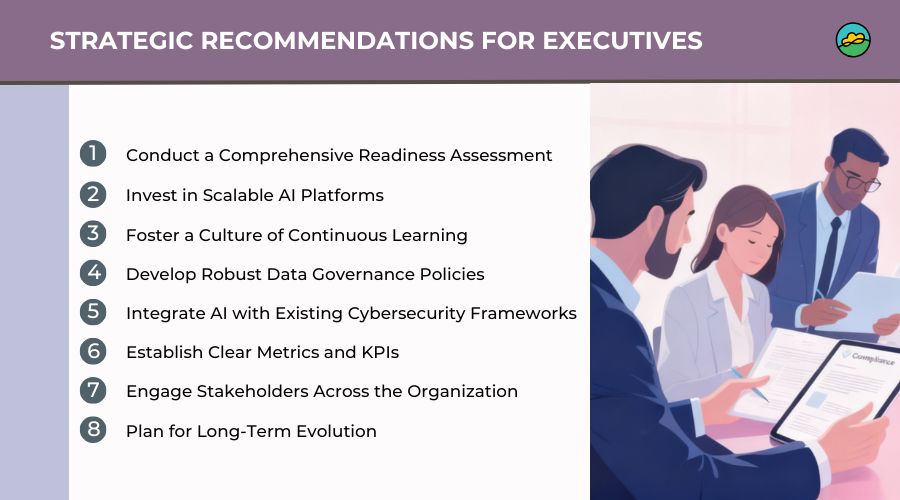
To successfully integrate AI-powered platforms into your compliance strategy, executive leadership must adopt a multi-faceted approach that includes commitment, investment, and agile adaptation. Below are strategic recommendations designed to guide leaders in accelerating their CMMC readiness through AI integration.
- Conduct a Comprehensive Readiness Assessment
Before deploying any AI-powered solution, it is essential to perform a comprehensive audit of your current cybersecurity posture relative to CMMC requirements. Identify gaps in existing security controls, compliance documentation, and incident response capabilities. This initial assessment will serve as the foundation upon which AI strategies can be built. Engage with internal experts and external consultants to ensure that the evaluation is thorough and aligned with both current and future regulatory demands. - Invest in Scalable AI Platforms
Choose AI platforms that are designed with scalability in mind. As your organizational needs evolve, your AI solutions should be capable of handling increased volumes of data, more complex threat analyses, and additional integration points from diverse systems. Consider solutions that offer flexible APIs, robust machine learning models and seamless integration capabilities with legacy infrastructure. This will not only ensure a smoother transition to AI-driven compliance but also provide long-term benefits as the threat landscape and regulatory requirements continue to evolve. - Foster a Culture of Continuous Learning and Innovation
Transformation through AI is not merely a technological change; it is a cultural shift. Executives must prioritize a culture of continuous learning and innovation. Encourage cross-functional teams to critically assess the performance of AI systems, share insights, and continuously refine processes. Invest in training programs that empower staff to effectively leverage AI tools and promote collaboration between cybersecurity, IT, compliance, and business units. A culture that embraces technology and innovation paves the way for resilient cybersecurity practices. - Develop Robust Data Governance Policies
Data is the lifeblood of AI-powered solutions. To fully capitalize on AI’s potential, organizations must establish robust data governance frameworks that ensure data quality, integrity, and security. Develop policies that clearly outline data collection, storage, processing, and sharing protocols. By doing so, you can safeguard against inaccuracies that may lead to compliance lapses and ensure that your AI algorithms are fed high-quality data. Transparency in data management processes also helps in building trust among auditors and regulatory bodies during the CMMC evaluation process. - Integrate AI with Existing Cybersecurity Frameworks
AI should complement, not replace, traditional cybersecurity measures. Integrate AI systems with existing Security Information and Event Management (SIEM) tools, Endpoint Detection and Response (EDR) solutions, and Identity and Access Management (IAM) frameworks. Such integration creates a layered defense where AI enhances the overall efficiency and effectiveness of cybersecurity strategies. This integrated approach ensures that AI-driven insights are actionable and that remedial actions are executed seamlessly, thereby reducing complexity and improving compliance outcomes. - Establish Clear Metrics and KPIs
To measure the effectiveness of AI in accelerating CMMC readiness, establish clear metrics and Key Performance Indicators (KPIs). Metrics might include the reduction in incident response times, improvements in data accuracy, the number of automated compliance reports generated, and the overall reduction in audit findings. Regularly review these KPIs to assess progress, make data-driven improvements, and align outcomes with strategic objectives. This level of accountability not only reinforces AI investment value but also drives continuous improvement in your compliance strategy. - Engage Stakeholders Across the Organization
Successful integration of AI systems relies on broad organizational buy-in. Ensure that stakeholders from all relevant departments IT, cybersecurity, operations, and executive leadership, are engaged in the transformation process. Regular briefings, cross-departmental workshops, and collaborative strategy sessions can dispel uncertainties associated with AI adoption. Clear communication helps in aligning goals, clarifying roles, and ensuring that the organization moves in unison toward achieving CMMC compliance. - Plan for Long-Term Evolution
AI and cybersecurity landscapes are continuously evolving. Adopt a long-term perspective by planning for future updates and enhancements to your AI systems. Just as CMMC requirements are continually refined based on emerging threats, your AI strategies should be viewed as an ongoing initiative. Allocate resources for research and development, pilot new technologies, and remain agile enough to pivot to new methods as the compliance landscape evolves. Embracing change is key to sustaining excellence in both cybersecurity and regulatory compliance.
Read the “AI-driven GRC automation: Enhancing governance with intelligent systems” article to learn more!
AI’s role in proactive risk management
One of the cornerstones of an effective cybersecurity strategy is proactive risk management. AI offers a significant leap forward by reducing the time between threat detection and response. Rather than relying solely on periodic audits or the slow pace of manual oversight, AI-based systems enable organizations to monitor their networks continuously, detecting anomalies and reacting in real time.
In practical terms, this means that organizations can deploy AI to predict potential security breaches. For example, by analyzing traffic patterns and user behaviors, AI can identify suspicious activities that might indicate a cyberattack. This early warning system is invaluable for maintaining the robust defense posture required for CMMC compliance.
AI can also automate the process of updating risk profiles as new data becomes available. This dynamic risk assessment allows organizations to stay ahead of emerging threats and continuously adapt their defenses, a critical advantage when adhering to the standards and audits mandated by CMMC.
The predictive power of AI doesn’t stop at prevention; it plays a substantial role in incident response as well. When a potential threat is detected, AI-driven systems can execute predefined response strategies, quarantining compromised systems or alerting cybersecurity teams before widespread damage occurs. Such automated responses free up valuable time for IT professionals, allowing them to focus on more complex security challenges.
Case study: A transformative journey with AI-driven compliance
Consider the case of a mid-sized defense contractor tasked with securing its digital infrastructure to meet CMMC requirements while facing resource constraints. The organization embarked on a comprehensive AI integration project that began with a deep-dive compliance assessment and a strategic selection of a scalable AI platform.
Within the first six months, the contractor witnessed a significant transformation in its compliance posture. Continuous monitoring systems, powered by machine learning algorithms, identified anomalies in real time. Automated reporting processes replaced weeks of manual documentation, while a predictive analytics module flagged potential vulnerabilities well before they could be exploited. The tool’s integration with legacy systems was carefully managed through incremental upgrades and API bridges, ensuring continuity and minimal disruption.
Ultimately, the organization reduced its incident response time by over 40%, improved audit outcomes, and demonstrated a proactive security posture that instilled confidence among DoD auditors. This case stands as a testament to the transformative impact of AI-powered platforms on accelerating CMMC readiness in a competitive, ever-evolving environment.
Prepare to pass your CMMC audit
A successful CMMC audit shows customers and prospects that you’re serious about protecting their data. TrustCloud helps you achieve CMMC certification faster, with less stress on each subsequent audit.
Future perspectives and benefits for DoD success
As technology continues to evolve, the future for AI-powered cybersecurity is brimming with promise. The DoD and its defense contractors are uniquely positioned to benefit from advances in artificial intelligence. Looking ahead, the integration of AI into cybersecurity operations is expected to become ever more sophisticated, incorporating elements such as deep learning, real-time threat intelligence, and autonomous response mechanisms.
Future perspectives in this field point towards enhanced interoperability between different cybersecurity tools and frameworks. An interconnected ecosystem where AI systems not only monitor but also predict threat vectors will further reinforce an organization’s defense posture. Moreover, as regulatory bodies continue to refine compliance standards like CMMC, AI’s ability to adapt quickly to changing requirements will prove invaluable for maintaining compliance and fostering innovation.
The benefits for DoD success extend beyond mere compliance. A robust, AI-empowered cybersecurity framework contributes directly to a stronger national defense by ensuring that sensitive data remains secure from cyberattacks. It also instills a culture of proactive risk management and continuous improvement, a culture that is essential for organizations operating in an increasingly digital and interconnected global environment.
Summing it up
Implementing AI-powered platforms to accelerate CMMC compliance is not merely a trend; it is a strategic imperative that positions organizations ahead of the curve in a constantly evolving digital landscape. By leveraging advanced analytics, automated reporting, and predictive threat intelligence, organizations can not only meet the rigorous standards set forth by the DoD but also establish a resilient and agile defense against emerging cybersecurity challenges.
For executive leadership tasked with guiding their organizations through this transformative era, the road ahead is clear: embrace technology, invest in scalable solutions, and foster a culture where innovation and excellence in cybersecurity are paramount. In doing so, you not only accelerate compliance readiness, but you also build a foundation for a robust and secure future.
Frequently asked questions
How can AI-powered platforms streamline CMMC readiness?
AI-powered platforms accelerate CMMC readiness by automating key compliance tasks that would otherwise be labor-intensive and error-prone. Instead of manually tracking control requirements, evidence, and gaps across documents and systems, AI tools ingest policies, log data, and configurations to identify compliance status in real time. They can automatically flag missing controls, generate audit-ready reports, and even suggest remediation steps tailored to CMMC levels.
These platforms support continuous monitoring, ensuring that changes in network posture or software configurations trigger alerts before issues escalate. Additionally, AI-assisted dashboards help executives track progress against milestones, allocate resources effectively, and prepare for external audits more confidently.
The result: compliance becomes an integrated workflow rather than a disruptive end-of-period scramble.
What challenges might organizations face when adopting AI for CMMC compliance?
While AI solutions offer significant advantages, they also present challenges that require careful planning.
First, integrating AI with existing IT and security tools can be complex; organizations must ensure data flows correctly from clouds, endpoints, and identity systems. Second, teams may need training to understand AI-generated insights and act appropriately. Without adoption and trust in the tool, AI potential remains untapped. Third, AI platforms must stay up-to-date with evolving CMMC requirements, meaning vendors need agile update cycles.
Finally, security and privacy considerations arise: AI tools themselves must be hardened and configured to prevent placing sensitive evidence at risk. Addressing these challenges upfront ensures AI integration adds value, not friction.
Why is investing in AI-enabled CMMC leadership a competitive edge?
Investing in AI-enabled CMMC compliance transforms a defensive requirement into a strategic advantage. First, it speeds up time-to-certification, allowing teams to win contracts faster. Contracts often hinge on timely CMMC levels, and businesses that demonstrate readiness earlier can outpace competitors. Second, AI supports ongoing compliance—meaning businesses avoid costly lapses and audit fatigue. Third, AI-driven reporting and dashboards communicate maturity and investment in security posture, boosting trust with DoD partners.
This trust translates into better positioning in RFPs, stronger partnerships, and long-term credibility. Essentially, AI makes CMMC compliance a foundation for business resilience and growth—not just an operational cost.
What are the core AI-driven strategies for transforming compliance processes in the defense industry?
There are several core strategies that leverage AI in the CMMC compliance journey:
- Automated data analysis & continuous monitoring
AI ingests logs, network traffic, and system alerts to detect deviations and vulnerabilities in real time. - Enhanced identity & access management (IAM)
AI learns user access patterns, flags anomalies, and supports layered authentication to protect sensitive information. - Intelligent incident response & remediation
AI platforms correlate alerts, prioritize based on severity, and trigger predefined response workflows, reducing response time and aligning with CMMC’s timely remediation expectations.
Together, these strategies enable a shift from periodic compliance checks to continuous assurance, ideal for dynamic defense industry requirements where data protection is both regulatory and mission-critical.
How should executive leadership approach integrating AI platforms into their CMMC compliance strategy?
The success of AI integration depends heavily on executive sponsorship and a multi-faceted approach. Key recommendations include
- Conduct a comprehensive readiness assessment to establish your baseline and gaps before selecting AI tools.
- Invest in scalable AI platforms that can grow with your data volumes, system complexity, and threat landscape.
- To foster a culture of continuous learning and innovation, employees must be trained to interpret AI insights and adapt processes accordingly.
- Develop robust data governance policies to ensure quality, integrity, and security of the data feeding AI systems; weak data undermines AI value.
- Integrate AI into existing cybersecurity frameworks (SIEM, IAM, EDR) rather than working in isolation, achieving layered defense and compliance alignment.
- Establish clear metrics and KPIs (such as reduction in incident response time, number of audit findings, and automated report generation) to evaluate AI investment and track compliance progress.
By aligning leadership, process, and technology and treating AI not just as a tool but as a strategic enabler, executives can turn CMMC compliance into a competitive differentiator rather than a regulatory burden.
